gametheory
[GAME THEORY] Who Can Revoke a Spyware Buyer's Reach?
Ad exchanges can cut a spyware facilitator's reach. Decide what that buys your high-risk users—and what still needs protection.
gametheory
Ad exchanges can cut a spyware facilitator's reach. Decide what that buys your high-risk users—and what still needs protection.

gametheory
Integrity Tech’s scanning-to-collection model puts the decision on attack-path ownership, not another attribution desk.
gametheory
Integrity Tech's capability mix changes the investment question: which routes to mail and identity remain after remediation?
gametheory
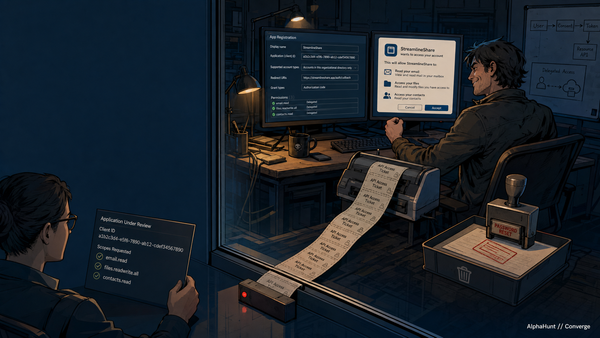
The attacker wants a durable app grant, not a password. Decide who can consent, what needs review, and how you prove revocation.
gametheory
A new joint advisory links recruiter malware and some DPRK IT workers. Here is where to join hiring, access, and payment decisions.
gametheory
The attacker needs sustained, useful output. Defenders can turn that dependency into friction across the access ecosystem.
gametheory
Shared intrusion logistics can be a better chokepoint than one APT—if defenders can prove real control-plane dependence.
gametheory
Vishing works because urgency can become SaaS authority. Break the trust transaction without breaking support.
gametheory
RaaS wins on repeatable access and recovery pressure. Here is how defenders can break the cheap path before encryption.
gametheory
MCP tool metadata can become routing logic. Here is who should re-approve changes—and what runtime controls must still decide.
gametheory
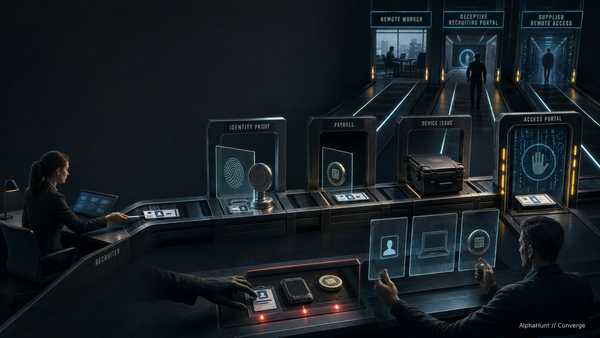
State-linked actors are competing for workforce trust. Map the handoffs that create access before the SOC sees an employee.
gametheory
Device-code phishing turns a legitimate login flow into rented access. The durable defense is to shrink who can use it.