[GAME THEORY] The Model Was Not Breached. It Was Mined.
The attacker needs sustained, useful output. Defenders can turn that dependency into friction across the access ecosystem.
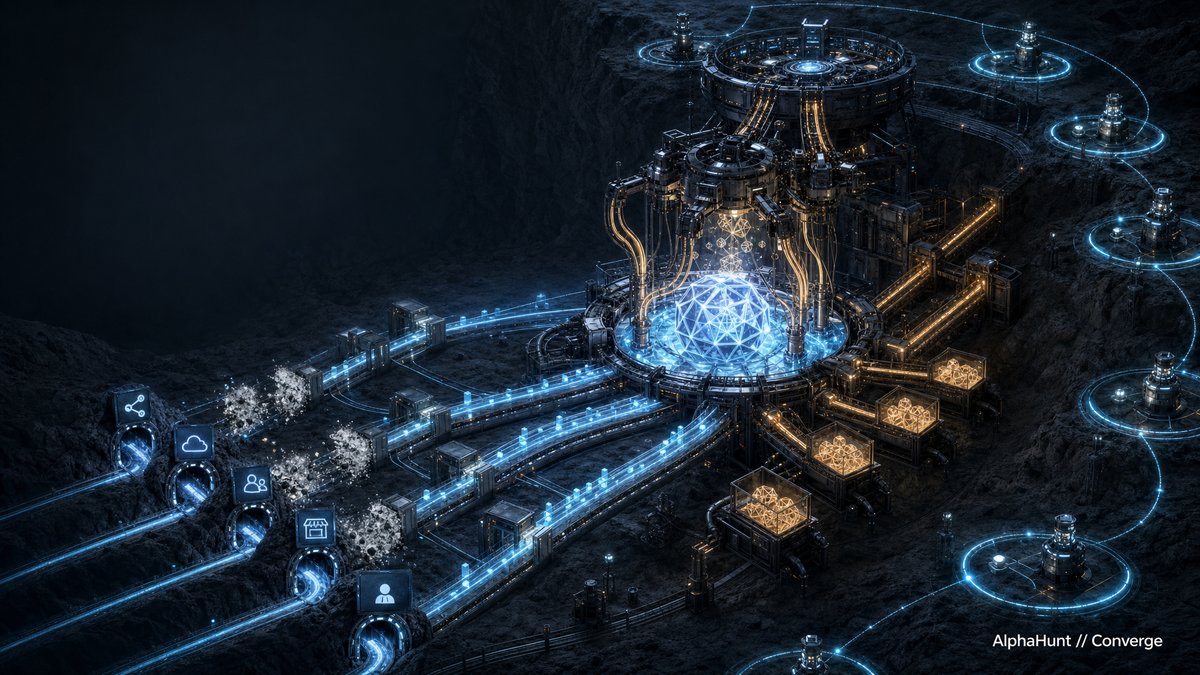
The strategic risk in industrial-scale model distillation is not a dramatic breach. It is that legitimate API access can become a standing collection channel for extracting valuable capability at a fraction of the cost of building it independently.
That puts defenders in an uncomfortable game. Block one account and the collector can rotate to another. Tighten one provider and traffic can move through a cloud endpoint, reseller, aggregator, or rival model. The practical payoff is a better unit of analysis: stop judging isolated prompts and start mapping the campaign that sustains throughput.
The model endpoint looks like a product surface. At sufficient scale, it can behave like a collection target.
TL;DR
- On September 8, 2026, CISA, NSA, and the FBI alleged that China-based AI companies used industrial-scale knowledge-distillation campaigns against U.S. frontier models. The advisory names DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI.
- The stronger CTI frame is not simply “AI companies copied models.” It is an adaptive collection operation built around accounts, payment methods, proxies, cloud routes, resellers, request orchestration, and quality testing.
- We assess that coalition friction is the strongest long-run lever because it reduces the collector’s ability to substitute one access path for another. Telemetry, access controls, and usage economics make that coalition actionable.
- The defender does not need to classify every act of distillation as malicious. The useful threshold is coordinated, concealed, evasive collection designed to extract differentiated capability at industrial scale.
- Measure reconstitution cost, not account bans. A campaign is being degraded when it becomes slower, less reliable, more expensive, and harder to rebuild across providers.
The key judgment
Model capability extraction should be treated as a repeated intelligence-and-economic competition, not only as an intellectual-property dispute or terms-of-service problem.
Observed: the CISA/NSA/FBI advisory describes centralized request routing across native APIs, cloud providers, aggregators, relays, and vendor account pools. It also describes automated failover, systematic quota and cost optimization, rapid route switching, and quality evaluation intended to detect defensive countermeasures. These are U.S. government allegations, not judicial findings.
Observed: Anthropic separately reported large-scale campaigns involving synchronized traffic, shared payment methods, fraudulent accounts, several access pathways, and a proxy network managing more than 20,000 accounts. Google reported detecting and disrupting model-extraction attempts from private-sector entities and researchers, while saying it had not observed direct frontier-model attacks by APT actors in the activity it described. Both are first-party provider accounts with unique visibility and commercial interests.
Assessed: the collector’s advantage comes from turning a retail access system into a distributed acquisition pipeline. The provider’s advantage comes from the same fact. Useful extraction requires repeated access, reliable throughput, high-value outputs, orchestration, and feedback about output quality. Those dependencies create observable and disruptable behavior.
Unknown: public reporting does not establish how much of any named company’s final model capability came from extracted output, what independent development contributed, or how much the reported disruption changed training outcomes. Those uncertainties matter. “Distillation occurred” is not the same claim as “distillation determined the capability gap.”
The game behind the endpoint
The players are optimizing for different outcomes.
Frontier-model providers want to sell broad access while protecting differentiated capabilities, safety controls, and customer trust. Controls that add friction can also reduce legitimate use, slow research, and push revenue elsewhere.
Extractor firms want useful capability below the cost and time of independent frontier training. Their ideal pipeline has sustained throughput, diverse access routes, predictable output quality, and enough concealment to survive enforcement.
A state sponsor or aligned institution may value accelerated domestic capability, reduced foreign dependence, and access to reasoning or tool-use behavior. It may also tolerate financial and organizational costs that would deter an ordinary commercial abuser.
Cloud providers, resellers, aggregators, payment processors, and proxy operators want demand without inheriting fraud, contractual, regulatory, or reputational risk. They can become the routes through which provider-specific controls lose force.
Governments want to protect strategic capability while preserving lawful research, commerce, competition, privacy, and due process. Attribution is hard, jurisdiction is uneven, and a broad restriction can harm the same ecosystem it is meant to defend.
The collective-action problem is the center of the game: one provider can pay the cost of tighter controls while the collector simply shifts to a less restrictive route. The attacker shops for the cheapest open lane. A coalition changes the price of switching lanes.
What each side is likely to do next
Provider move: tighten identity and throughput controls
Providers can require stronger provenance for high-volume access, link accounts through payment, device, timing, and infrastructure signals, and apply progressive throttling to suspicious clusters.
Collector countermove: fragment the campaign
Expect more account farms, front companies, stolen credentials, intermediaries, residential proxies, regional distribution, and low-and-slow collection. The collector can also divide tasks among providers so no single service sees the entire acquisition plan.
Provider move: detect training-relevant behavior
Providers can look for sustained automated use, synchronized task patterns, rapid quota exhaustion, unusual model switching, repeated quality evaluation, and collection concentrated on differentiated capabilities.
Collector countermove: make legitimate use the camouflage
The collector can mix extraction traffic with ordinary requests, vary prompts, sanitize metadata, and route through shared commercial infrastructure. Content alone becomes a weak signal.
Coalition move: correlate campaigns across access paths
Providers, cloud platforms, aggregators, and relevant authorities can share high-confidence behavioral and infrastructure indicators under narrow legal and privacy controls. The goal is not a universal customer dossier. It is to recognize when apparently separate anomalies are one coordinated operation.
Collector countermove: reduce dependence on proprietary APIs
Open-weight models, domestic systems, synthetic-data pipelines, and local generation can reduce exposure to provider controls. If those substitutes become good enough, blocking frontier API access may displace collection rather than slow capability acquisition.
Practical gut-check: if one provider blocked the campaign tonight, how much of its useful throughput would be restored through another route by morning?
Below the tear line: how to separate strategic extraction from ordinary model use, which signals reveal adaptation, and one campaign-level review defenders can run this week. We also include the technical Game Theory report.
Which part of your model-access ecosystem would let a blocked collector restore high-volume capability fastest—and who outside your team would need to help close it?
Signal vs. noise
Distillation is a legitimate machine-learning technique. High usage is not proof of espionage. A prompt asking for code, reasoning, benchmarks, or structured output is not evidence of malicious extraction by itself.