[GAME THEORY] Who Can Revoke a Spyware Buyer's Reach?
Ad exchanges can cut a spyware facilitator's reach. Decide what that buys your high-risk users—and what still needs protection.
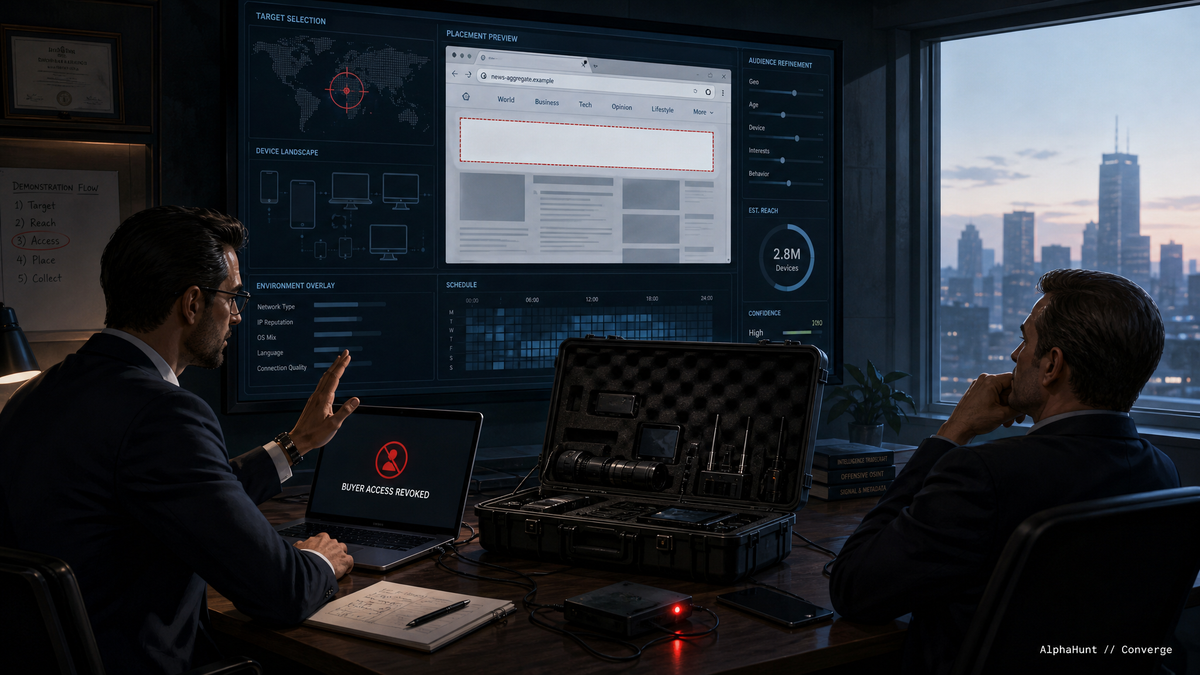
An ad exchange can stop a spyware facilitator buying impressions. It cannot patch the people who already saw them.
Citizen Lab's October 15 AdFection investigation links targeted advertisements purchased by Discover-Tech to historical Candiru spyware infections at Al Jazeera. Early-October platform actions interrupted parts of that distribution system. The question now is what those exclusions actually removed. [1]
Our judgment: Exchange exclusion cuts reach and channel-specific code staging; treat it as meaningful containment, not proof that the whole spyware capability is gone.
That distinction changes a practical decision: protect high-risk browsing now, then reassess the investment in April 2027 against evidence of capability loss or return—not the length of a vendor's removal notice. April is our proposed review point, not a deadline imposed by the research.
The reviewed reporting does not establish a linked delivery chain after disconnection. This is not a claim that the operation migrated. It is a way to avoid confusing an interrupted route with either eradication or proven survival.
A rendered ad is an opportunity, not an infection count
Discover-Tech's delivery mechanism made an ordinary ad slot useful to a spyware customer. After an impression, an embedded script contacted operator-controlled infrastructure with device and advertising context. The server could return additional JavaScript—or nothing. That let the operator choose what to stage after reaching the browser. Target identification could also begin earlier, using information in the advertising auction. [1]
Confiant's companion investigation describes an encrypted command channel and JavaScript compiled through new Function(...). Its important limit: the code ran with the authority of its execution context, here an ad frame. That is not, by itself, browser escape or spyware installation. Citizen Lab provides the separate historical victim-side evidence connecting ad delivery, Candiru validation infrastructure and subsequent command-and-control traffic. The investigations are partners, not two wholly independent confirmations of every step. [1, 2]
Here is a useful check before closing an alert: label the evidence as ad delivery, identity matching, selective staging or compromise. A suspicious ad request deserves investigation; it does not establish all four. Conversely, removing the buyer does not establish that all four ended.
The continuation turns that distinction into a working choice: which controls change the operator's options, and what evidence would justify relying more heavily on supplier exclusion at renewal.
The buyer needs access that someone else can revoke
The contest is less about an invulnerable exploit than about who controls the next opportunity to put it near a selected device.