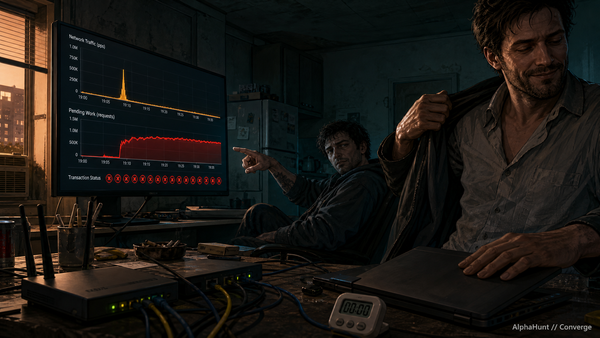
[DEEP RESEARCH] The Attack Ended Before the Escalation Did
Short DDoS bursts can outlast their traffic. Test when customers recover—not when a provider declares mitigation active.
Short DDoS bursts can outlast their traffic. Test when customers recover—not when a provider declares mitigation active.
Patch the Ivanti chain without mistaking it for recovery; separate AI workflow acceleration from stolen model access.
Virtualine promised to move customers after law-enforcement requests. Test who can restore the service—not just who registers next.
The core judgment stays free. Reader adds the full analysis and research.
Crime Stoppers suspensions expose the question a sanitized investigator copy cannot answer: what did the platform keep?
Check the access that survives a password reset, a PHP patch, or a browser trust update.
Ad exchanges can cut a spyware facilitator's reach. Decide what that buys your high-risk users—and what still needs protection.
French refrigeration hacks expose a maintenance gap: prove safe settings, controlled access and recovery before renewal.
Reconstruct short update-tampering windows, trace edge access into virtualization, and separate payload blocking from credential access.
Resource-themed espionage is not proof of industrial access. Protect the planning data—and know what would change the assessment.

Integrity Tech’s scanning-to-collection model puts the decision on attack-path ownership, not another attribution desk.
Edge-device upgrades do not prove eviction. Preserve evidence, check earlier access, and track real-time phishing beyond the inbox.
gametheory
Integrity Tech's capability mix changes the investment question: which routes to mail and identity remain after remediation?
gametheory
The attacker wants a durable app grant, not a password. Decide who can consent, what needs review, and how you prove revocation.
weekly
Trusted developer projects, cloud services, and stolen secrets are changing the containment problem.
deep
NetScaler shows why version compliance, compromise assessment, and restored trust are three different jobs.
gametheory
A new joint advisory links recruiter malware and some DPRK IT workers. Here is where to join hiring, access, and payment decisions.
weekly
Edge patching may close the hole but not remove access; this issue tracks service-principal abuse and integrator routes into OT.
forecasts
A 58% disclosure forecast—and the ownership test that matters before the next campaign is named.
deep
New NIST guidance exposes a containment gap: the revocation command can succeed while an attacker’s access survives.
weekly
The engineer called it internal; the attacker found it internet-adjacent. Inventory and patch exposed GS1900 and Conductor gear, then hunt job changes and secret access.
forecasts
Two incidents appear to clear the bar. Govern AI credentials by replay value and blast radius before access becomes impact.
deep research
A practical operating model for package admission, runtime detection, and proving downstream impact before the trail goes cold.
weekly
Patch the control plane, then hunt leaked authority: new admins, fresh tokens, API use from new origins. Copied keys can outlive a green patch dashboard.