[GAME THEORY] The help desk is becoming the new intrusion broker.
Vishing works because urgency can become SaaS authority. Break the trust transaction without breaking support.
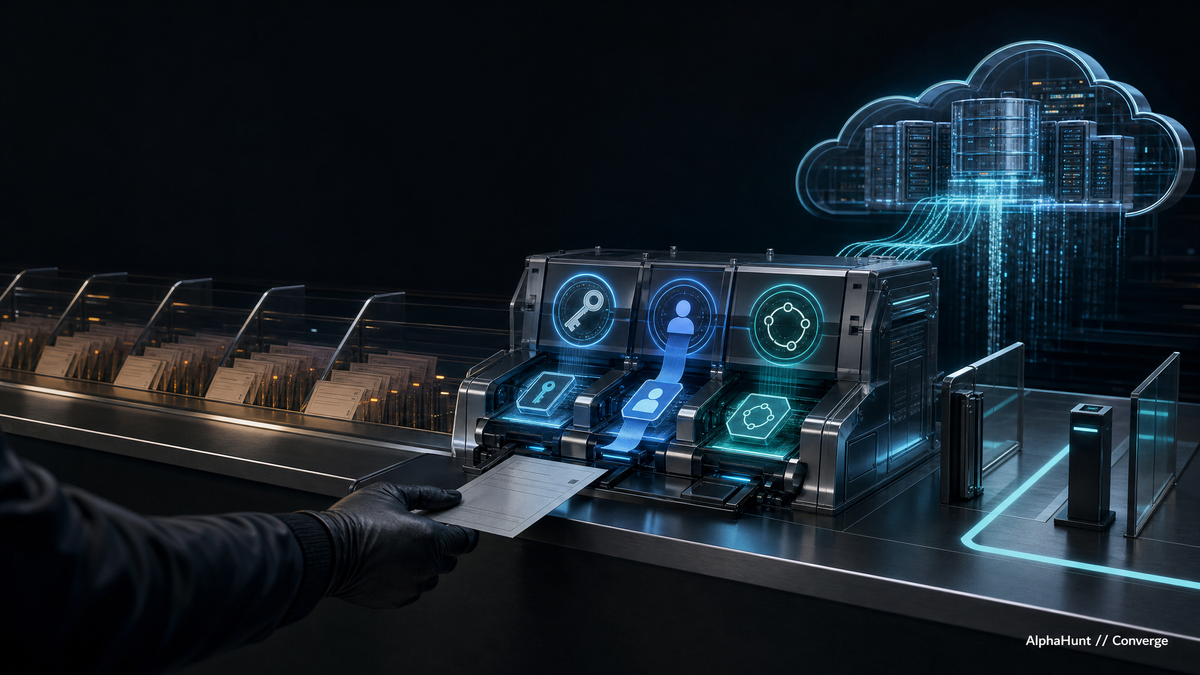
The help desk is not merely a side door. It is a market where urgency can be converted into enterprise authority.
Attackers have learned to pressure the people and workflows that reset passwords, enroll MFA factors, approve recovery, and steer users toward “support” applications. Defenders face an awkward tradeoff: slow every request and business operations suffer; optimize only for ticket closure and a convincing caller may leave with durable SaaS access. The practical move is not more generic awareness training. It is to identify each trust transaction, require independent evidence for consequential changes, and correlate the change with what happens next.
The phone call is the lure. The product is authority.
TL;DR
- Google reported that UNC6671 used help-desk vishing, adversary-in-the-middle portals, MFA-token interception, and automated cloud-data theft while operating through multiple extortion brands.
- Microsoft separately documented vishing-led malicious OAuth consent in which users authorized attacker-controlled applications presented as legitimate tooling.
- We assess that these operations exploit a market failure: support speed is rewarded locally, while the enterprise absorbs most of the downside when a trust decision is wrong.
- Help-desk recovery, AiTM session theft, and malicious OAuth consent are distinct paths. A single “MFA bypass” label hides different control boundaries and telemetry.
- Defenders get leverage by separating identity proof from authority changes, reducing the cost of independent verification, governing risky consent, and correlating trust changes with SaaS use.
The key judgment
The strongest attacker innovation here is not a new phishing kit or extortion brand. It is a repeatable way to turn institutional pressure into authorized access.
A support agent wants to resolve the ticket. An employee wants to comply with someone who sounds like security. An identity platform wants recovery to work. A SaaS vendor wants integrations to remain easy. An executive wants business friction kept low. Each incentive is reasonable in isolation.
The attacker arbitrages the seams.
That makes access a transaction rather than a single credential-theft event. The attacker presents a claim, manufactures urgency, supplies just enough evidence, and asks the defender’s process to mint something valuable: a password reset, a new MFA factor, an authenticated session, an OAuth grant, or a role change.
Google Threat Intelligence described UNC6671 as a financially motivated threat cluster that continued compromising organizations after BlackFile’s alleged retirement, used several extortion brands, and combined help-desk vishing, AiTM phishing, MFA-token interception, and automated exfiltration from Microsoft 365 and Okta environments. Microsoft separately reported vishing cases in which users were persuaded to authorize malicious applications disguised as a Salesforce Data Loader tool.
Observed: actors are using social pressure to obtain recovery changes, sessions, or delegated SaaS authority, then moving quickly toward cloud data.
Assessed: the repeatable advantage is the trust-conversion workflow, not any one brand, portal, or authentication trick.
Unknown: how much infrastructure and scripting the named crews share, and whether reported incidents represent one coordinated market or several groups converging on the same economics.
Three games hiding inside “vishing”
The common label is convenient. It is also analytically dangerous.
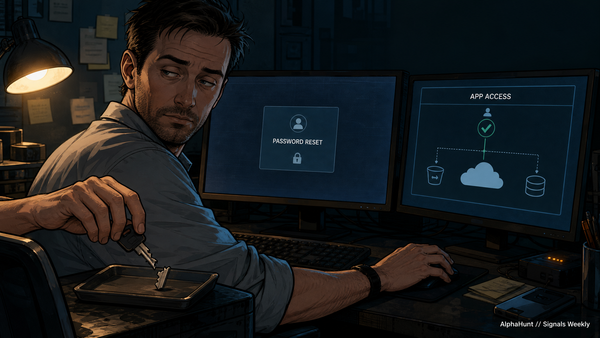
1. Help-desk recovery vishing
The attacker impersonates an employee and persuades support to reset a password, change recovery information, enroll a new MFA factor, or initiate another recovery path.
The control boundary is the enterprise’s identity-proofing and recovery process. The useful telemetry begins with service-desk tickets and call records, then moves into password-reset, MFA-registration, recovery-data, role-change, sign-in, and SaaS audit events.
2. AiTM session theft
The attacker directs an employee to an adversary-in-the-middle portal that relays authentication to the real identity provider. The employee may complete MFA successfully while the attacker captures a usable session artifact.
No help-desk action or OAuth grant is required. The control boundary is the active authenticated session. Useful telemetry includes sign-in context, device state, conditional-access decisions, proxy or DNS evidence for a look-alike portal, and subsequent SaaS behavior that does not fit the original user or device.
3. Vishing-driven malicious OAuth consent
The attacker persuades a user to approve a purported support or migration application. The authorization service records the grant and issues tokens to the attacker-controlled client. The client can then call SaaS resources within the intersection of granted scopes, tenant policy, and the user’s underlying entitlements.
The control boundary is delegated authorization. Password resets alone may not remove it. Defenders need consent events, application and service-principal changes, publisher and redirect-URI context, granted scopes, and resource-side API activity tied back to the client or application ID.
Three paths. Three control boundaries. Three opportunities to avoid a vague “the user got phished” postmortem.
The incentive problem
For the frontline agent, fast handling has an immediate and visible benefit: the requester gets back to work, the queue moves, and service metrics improve. Independent verification has an immediate cost: more time, another person, a callback, or a frustrated employee.
The breach cost is delayed, uncertain, and mostly borne by someone else.
That is why “be more careful” is weak control design. It asks a tired person to absorb organizational friction while making a high-stakes judgment with incomplete information. Attackers can rehearse the script. The defender has to judge a single call in real time.
A better policy changes the payoff:
- make independent verification fast and routine;
- provide better signals to the decision-maker;
- prevent one pressured interaction from both proving identity and granting consequential authority;
- measure safe resolution, not only closure speed;
- correlate the trust change with the access and collection that follow.
Practical gut-check: which request in your support queue can create the most authority with the least independent evidence?
Below the tear line: how attackers and defenders are likely to adapt, which signals matter, and the one workflow change worth testing this week.
We also include the technical report.
Which team owns the full sequence from a high-risk support request to the next SaaS export—and can that team reconstruct it before the attacker finishes collecting?
Moves and countermoves
Defender move: require verified recovery
Use a directory-sourced callback, authenticated self-service channel, managed-device confirmation, or independent approval for high-risk recovery and identity changes. Do not trust contact details supplied inside the same inbound interaction.
Attacker countermove: target the verification channel
Expect crews to pursue personal devices, compromise contact records, impersonate vendors, or tailor scripts to the organization’s exact support workflow. Generic portals are easy to replace. Process knowledge is the more durable asset.
Defender move: restrict risky consent
Limit user consent for high-risk scopes, require review for sensitive or administrative grants, maintain approved-app ownership, and remove unused applications and grants.
Attacker countermove: improve the app story
Expect better branding, plausible migration pretexts, compromised or look-alike publishers, and scripts that move users toward applications whose requested permissions sound operationally reasonable.
Defender move: make sessions conditional
Use phishing-resistant MFA for privileged and recovery roles where supported. Apply device, network, session, and risk controls so a captured session is less portable.
Attacker countermove: stay closer to the user
Expect more use of browser-based interaction, residential infrastructure, remote-control tooling, or activity timed to legitimate sessions. The attacker does not need to look normal forever—only long enough to create or exercise authority.
This is a game of substitution. Hardening one path can make another relatively more attractive. Recovery, session, and OAuth controls must be treated as separate but connected systems.
Signals to watch
The access market is getting more efficient if:
- incident reports show process-specific help-desk scripts rather than generic security pretexts;
- new victim-branded AiTM portals appear alongside support impersonation;
- suspicious OAuth grants are followed quickly by API enumeration, mailbox access, file collection, or bulk export;
- multiple extortion brands reuse infrastructure, victimology, client IDs, social scripts, or exfiltration automation;
- actors increasingly target personal devices or vendor relationships to defeat enterprise verification;
- public cases show recovery changes, new sessions, and SaaS collection compressed into shorter timelines.
Defender pressure is working if:
- verified callbacks or independent approval stop high-impact recovery attempts without making ordinary support unusable;
- high-risk consent moves from user discretion into reviewed workflows;
- teams routinely revoke illicit grants and assignments rather than stopping at password resets;
- identity, service-desk, and SaaS telemetry can be joined quickly around one trust-change event;
- captured sessions fail because device or conditional-access requirements do not travel with them;
- support metrics reward verified resolution and post-recovery safety.
Strategy-shift signal
Watch for attackers abandoning generic portals in favor of scripts built around a target’s actual support, recovery, and application-approval procedures. That would indicate the market is professionalizing around process intelligence.
What defenders should do now
1. Inventory trust transactions
List the actions that materially increase authority: password reset, recovery-data change, MFA enrollment, role activation, device registration, OAuth consent, service-principal assignment, and emergency access.
Assign an owner, evidence requirement, and audit source to each one.
2. Separate identity proof from authority
Do not let one inbound conversation both establish identity and authorize a high-impact change. Require an independent channel or approver when the requested action can create durable access.
The goal is not maximum friction. It is friction that the attacker cannot manufacture inside the same script.
3. Correlate the before and after
Join support events with identity and SaaS activity. Prioritize sequences such as:
- inbound support contact → password reset → new device or session → bulk download;
- recovery change → MFA enrollment → administrative role activation;
- consent event → new client ID → rapid API enumeration or export;
- successful MFA without recovery activity → unusual session or SaaS behavior.
No one has infinite time to chase every consent event. The sequence is where the signal improves.
4. Revoke the authority that was actually granted
For malicious OAuth consent, remove the illicit grant or service-principal assignment and investigate the application’s resource activity. A password reset may leave delegated access intact.
For suspected session theft, revoke sessions and evaluate how the session escaped device or network constraints. For recovery abuse, inspect every state change created during the interaction.
5. Tune the service metric
Measure verified resolution, repeat contact, exception use, high-risk recovery volume, and post-recovery anomalies—not only average handling time and ticket closure.
If the safe path always loses the queue metric, the policy is quietly paying agents to take risk.
One clean win
Pick one consequential recovery action this week—new MFA enrollment is a good candidate—and walk it end to end.
Ask:
- Can an inbound caller supply every fact used to verify identity?
- Does one person both approve the identity claim and create the new authority?
- Can you correlate the ticket with the MFA event, next sign-in, and subsequent SaaS activity?
Fix one gap that reduces verification effort or increases independence. Boring workflow engineering is how defenders make the attacker’s social script less profitable.
What would change our mind
We would weaken this assessment if credible incident reporting showed that the cited activity was mostly one-off clustering, with little reuse of support-process scripts, infrastructure, delegated authorization, or cloud collection patterns.
We would strengthen it if victim reporting, law-enforcement records, or vendor telemetry showed repeated reuse of process-specific scripts across extortion brands, or if attackers consistently chained trust changes to automated SaaS collection within the same operating model.
Why this is beatable
The attacker still needs a person or system to accept a claim, create authority, and let that authority touch valuable resources. They need the verification channel to remain dependent on information they can supply. They need the trust change to blend into normal support. They need the session or grant to survive long enough to collect data.
Those are dependencies, not magic.
Make independent verification cheap. Separate proof from authority. Govern risky consent. Bind sessions to context. Correlate the ticket with the access that follows. The attacker can change the script, but they cannot cash out without touching a trust boundary defenders can instrument.
Forwardable line: attackers do not need stronger malware when one urgent conversation can mint durable authority.
Defender takeaway
Model recovery, authentication, and delegated authorization as separate trust-conversion paths. Then connect their telemetry around the moment authority changes.
The help desk does not have to become an intrusion broker. But the enterprise has to stop paying it only for speed.
Appendix
References
- Google Threat Intelligence Group, “UNC6671 Rebrands: Multi-Brand Vishing Extortion Targets Financial Services and Enterprise Cloud Environments,” August 6, 2026. https://cloud.google.com/blog/topics/threat-intelligence/unc6671-targets-financial-services-and-enterprise-cloud-environments
- Microsoft Security Blog, “Defending SaaS-based applications against ShinyHunters OAuth abuse,” July 13, 2026. https://www.microsoft.com/en-us/security/blog/2026/07/13/defending-saas-based-applications-against-shinyhunters-oauth-abuse/
- Microsoft Learn, “Detect and remediate illicit consent grants in Microsoft 365,” July 3, 2026. https://learn.microsoft.com/en-us/defender-office-365/detect-and-remediate-illicit-consent-grants
- Microsoft Learn, “Require phishing-resistant multifactor authentication for Microsoft Entra administrator roles,” March 24, 2026. https://learn.microsoft.com/en-us/entra/identity/conditional-access/policy-admin-phish-resistant-mfa
AlphaHunt
Stop doomscrolling, start decisioning. We chewed through the muck so your team doesn’t have to. → Subscribe! • Forward to your on-call lead.
(Have feedback? Did something resonate with you? Did something annoy you? Just hit reply! :))
(c) 2026 CSIRT Gadgets, LLC