[SIGNALS WEEKLY] Edge Compromise, Real-Time Phishing, and Evidence Gaps
Edge-device upgrades do not prove eviction. Preserve evidence, check earlier access, and track real-time phishing beyond the inbox.
TL;DR
- [Vulnerabilities] Concurrent, high-impact bugs on internet-facing edge/control-plane systems (Citrix NetScaler, Cisco SD-WAN Manager, Atlassian DC, GitLab) demand pre-patch compromise checks and deliberate log preservation, not “patch and forget.”
- [Threat Actors] China-linked operators are pairing mass automated scanning with targeted, hands-on intrusion to steal email and credentials from critical infrastructure, using compromised edge devices as durable footholds.
- [Phishing] Adversary-in-the-middle kits leveraging QR lures and real-time WebSocket-driven Google login orchestration are eroding MFA protections and pushing credential theft beyond email into physical/event-driven vectors.
Current Stories
TL;DR
- [Vulnerabilities] Edge/control-plane patch sprint: High-impact issues across Citrix NetScaler, Cisco SD-WAN Manager, Atlassian Data Center, and GitLab self-managed are compressing patch windows and raising “validate before/after upgrade” pressure.
- [Intrusion Sets] China-linked operations at scale: Joint advisory describes China-aligned activity “enabled” by Integrity Technology Group, combining automated scanning with hands-on intrusion to steal email and credentials from critical infrastructure.
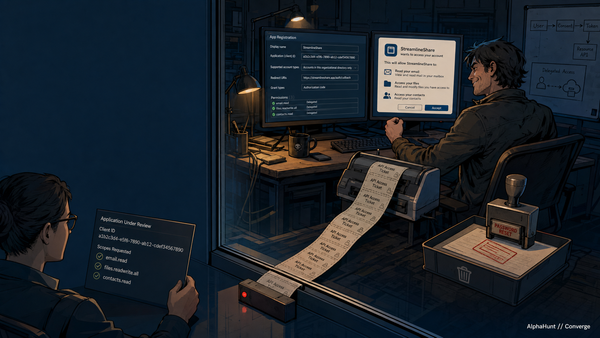
- [Phishing] AitM + QR (“quishing”) is operationalized: Taiwan-focused spear-phishing uses event-themed lures plus real-time adversary-in-the-middle phishing against Google authentication flows to intercept credentials and MFA challenges.
References
- (2026-10-09) Critical Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC, Gateway | CISA
- (2026-10-08) Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data | CISA
- (2026-10-05) CVE-2026-21589 - Arbitrary File Access Vulnerability impacts Multiple Products | Atlassian
- (2026-10-12) GitLab Critical Patch Release: 19.4.2, 19.3.5, 19.2.8 | GitLab Docs
- (2026-09-30) Critical Cisco Catalyst SD-WAN Manager API authentication bypass exploited in the wild (CVE-2026-76504) | Rapid7
- (2026-10-08) UAT-11985: AI-assisted event lures delivering real-time Google AitM phishing | Cisco Talos
Emerging Stories
TL;DR
- [Vulnerabilities] “Patch isn’t proof” is becoming cross-vendor guidance (with concrete hunt hooks): CISA urges checking for compromise prior to patching NetScaler and preserving logs/evidence; Atlassian explicitly notes it cannot confirm impact and provides access-log hunting guidance; Cisco/Rapid7 guidance for SD-WAN Manager stresses auditing for compromise after emergency upgrades.
- [Phishing] What’s next beyond “AitM + QR”: operator-driven, real-time login orchestration will scale outside the inbox. Talos documents kits using hybrid HTTP POST + WebSocket to drive MFA screens in real time, plus link-text vs href mismatches (benign-looking Google Forms display text) and tampered event posters that can spread via printed materials/bulletin boards to secondary victims.
References
- (2026-10-09) Critical Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC, Gateway | CISA
- (2026-10-05) CVE-2026-21589 - Arbitrary File Access Vulnerability impacts Multiple Products | Atlassian
- (2026-09-30) Critical Cisco Catalyst SD-WAN Manager API authentication bypass exploited in the wild (CVE-2026-76504) | Rapid7
- (2026-10-08) UAT-11985: AI-assisted event lures delivering real-time Google AitM phishing | Cisco Talos
- (2026-10-08) Cisco-Talos/IOCs: uat-11985.txt (Indicators of compromise) | GitHub
Forecasts
TL;DR
- Short-term: Expect rapid exploitation attempts against exposed edge/admin planes; incident timelines will blur as compromise can predate patches and survive “upgrade-only” responses.
- Long-term: Real-time AitM kits will increasingly look like interactive “remote assistants” for login theft—pushing phishing beyond email into posters, QR handouts, and shared event collateral.
- Overlooked risk: Evidence loss during remediation: local appliance logs rotate quickly; upgrades and rebuilds can reduce forensic visibility if preservation isn’t done first.