deep
[DEEP RESEARCH] Who Owns the Cold Chain When the Controller Goes Online?
French refrigeration hacks expose a maintenance gap: prove safe settings, controlled access and recovery before renewal.
deep
French refrigeration hacks expose a maintenance gap: prove safe settings, controlled access and recovery before renewal.
weekly
Reconstruct short update-tampering windows, trace edge access into virtualization, and separate payload blocking from credential access.
deep
Resource-themed espionage is not proof of industrial access. Protect the planning data—and know what would change the assessment.

gametheory
Integrity Tech’s scanning-to-collection model puts the decision on attack-path ownership, not another attribution desk.
weekly
Edge-device upgrades do not prove eviction. Preserve evidence, check earlier access, and track real-time phishing beyond the inbox.
gametheory
Integrity Tech's capability mix changes the investment question: which routes to mail and identity remain after remediation?
gametheory
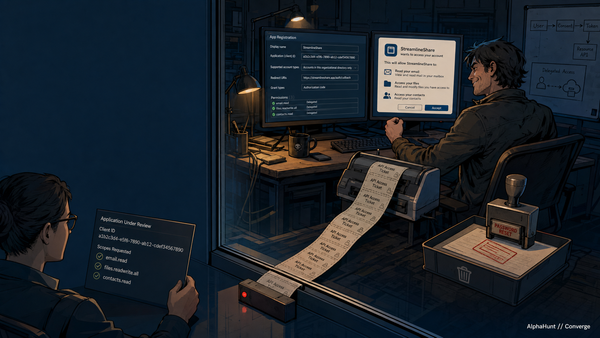
The attacker wants a durable app grant, not a password. Decide who can consent, what needs review, and how you prove revocation.
weekly
Trusted developer projects, cloud services, and stolen secrets are changing the containment problem.
deep
NetScaler shows why version compliance, compromise assessment, and restored trust are three different jobs.
gametheory
A new joint advisory links recruiter malware and some DPRK IT workers. Here is where to join hiring, access, and payment decisions.
weekly
Edge patching may close the hole but not remove access; this issue tracks service-principal abuse and integrator routes into OT.
forecasts
A 58% disclosure forecast—and the ownership test that matters before the next campaign is named.