[SIGNALS WEEKLY] Accelerating Threats in Trusted Digital Supply Chains
Trace the support, identity and software paths attackers can reuse—and check what survives your first cleanup.
The fast read
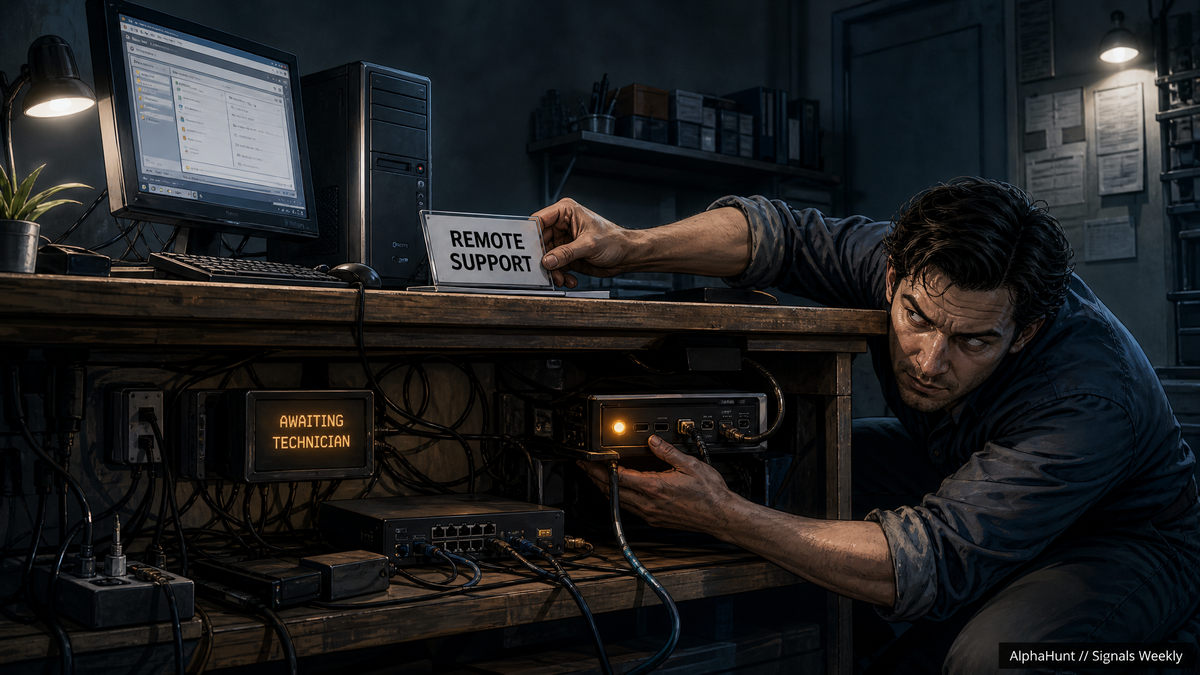
A compromised customer device can become a trap for the technician sent to help. Microsoft’s SCKit investigation describes malware deployed through ScreenConnect that adds unauthorized remote access and is designed to target connecting support staff. Separately, Cursor’s incident update traces stolen credentials into its extension-delivery cache, while Google details how COLD RELIC turns stolen correspondence into access to another organization. [1–3]
Our judgment: Prioritize the access that can carry an intrusion into the next device, account or organization—and verify that recovery removes it, not just the first visible symptom.
For teams using the affected support tooling, SCKit deserves immediate attention. For identity responders, COLD RELIC makes the case for checking attacker-enrolled authentication methods alongside sessions and OAuth grants. Optimizely’s JavaScript incident warrants an exposure check, not an assumption that every visitor was compromised. And Google’s agentic-threat reporting supports a narrower, more useful conclusion than “everything is autonomous now”: some operators are automating meaningful intrusion tasks, but prevalence and success still need evidence. [1,3–5]
SCKit makes the support connection part of the investigation
ScreenConnect has three distinct roles: the management server, the technician’s workstation and the customer endpoint. Treating them as one asset obscures what needs fixing.
Microsoft confirms abuse of ScreenConnect to install additional clients connected to attacker-controlled infrastructure and deploy SCKit on managed endpoints. The toolkit establishes persistence through scheduled tasks and registry Run entries. Its RelayTrap component is designed to deliver a payload to a technician who connects to an affected customer device with a vulnerable client. Browser-access and console-distribution components also target authenticated management sessions and the devices those accounts can reach. [1]
That is a propagation design, not proof that every affected endpoint infected a technician or that every accessible customer was compromised. Initial access also remains under investigation. Microsoft describes a reported authentication flaw in particular RMM+ extension versions and configurations; that server-side route is separate from RelayTrap’s endpoint-to-technician path. [1]
The distinction changes the response. Microsoft relays ConnectWise’s guidance that technician client version 26.6.5 and later blocks the attempted endpoint-to-technician transfer technique. Updating the cloud console does not automatically update those clients. Securing the server does not remove an unauthorized client already installed on an endpoint, and deleting that client does not invalidate an exposed browser session. [1]
If compromise is suspected, isolate affected endpoints and investigate through a separate, approved channel rather than using ScreenConnect on the affected device. Preserve console and endpoint records, include connecting technician workstations in scope, and follow the vendor’s guidance to keep the identified extensions disabled. Check client versions separately. [1]
From a clean device, invalidate affected ScreenConnect and associated identity-provider sessions, rotate exposed credentials, and review accounts and permissions. Remove malicious persistence and unapproved clients; inspect queued commands and Toolbox items before reconnecting. Verify the resulting state and rebuild where integrity cannot be established. Do not use the toolkit’s own cleanup script as your remediation tool. [1]
The support tool being legitimate is not the question. Which instance it answers to, what it executed and whose session it can reuse are.
The member continuation separates the identity and delivery paths worth checking next, then turns them into three focused investigations for this week.
COLD RELIC kept more than the password
Google’s linked case studies show why an account can look recovered while an attacker still has a way back in—or enough stolen context to approach the next victim.