weekly
[SIGNALS WEEKLY] Edge Brokers, Ephemeral Supply Chains, and Control-Plane Pivots
Reconstruct short update-tampering windows, trace edge access into virtualization, and separate payload blocking from credential access.
weekly
Reconstruct short update-tampering windows, trace edge access into virtualization, and separate payload blocking from credential access.
weekly
Edge-device upgrades do not prove eviction. Preserve evidence, check earlier access, and track real-time phishing beyond the inbox.
weekly
Trusted developer projects, cloud services, and stolen secrets are changing the containment problem.
weekly
Edge patching may close the hole but not remove access; this issue tracks service-principal abuse and integrator routes into OT.
weekly
The engineer called it internal; the attacker found it internet-adjacent. Inventory and patch exposed GS1900 and Conductor gear, then hunt job changes and secret access.
weekly
Patch the control plane, then hunt leaked authority: new admins, fresh tokens, API use from new origins. Copied keys can outlive a green patch dashboard.
weekly
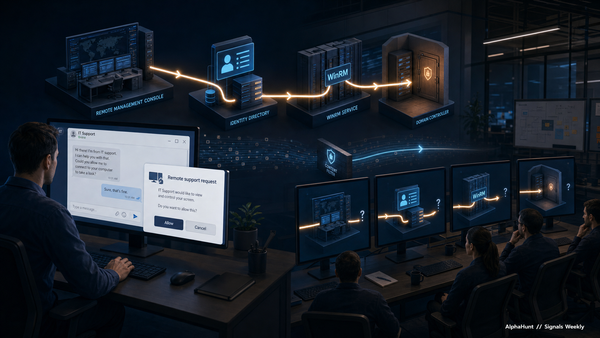
A Teams message from “IT” can now be the first step in a domain takeover: remote-support session, silent install, then AD and WinRM movement.
weekly
Three clocks are running: active PaperCut exploitation, QTFY infrastructure rebuilding after disruption, and AI-agent activity outpacing log governance. Hunt the transitions—not the tidy incident story.
weekly
The quiet failure mode in this week’s signals is trust doing exactly what it was configured to do—for the wrong operator. A TeamCity foothold can expose secrets and poison downstream artifacts..
weekly
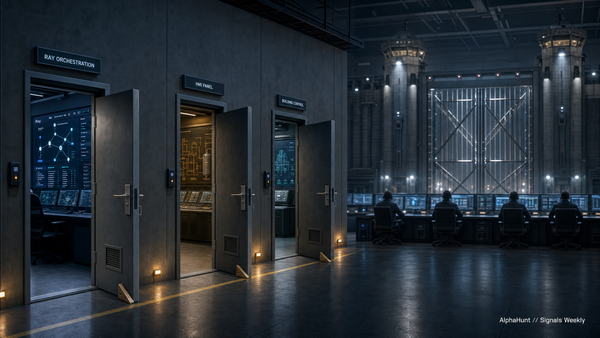
Exposed management planes are becoming the shortest path from ordinary web access to operational impact. Ray CVE-2025-62593 is now in CISA’s KEV, while new Haiwell and Metasys flaws put AI compute and OT interfaces on the same uncomfortable list.
weekly
Edge exploits, helpdesk vishing, stolen CI tokens, and decentralized C2 share one objective: scale access while shrinking defender visibility. Hunt the transitions, not just the opening IOC.
weekly
Some of this week’s most useful threat signals point to access paths that sit just outside the normal inventory: a cellular modem added by an OT integrator, a hotel captive portal steering a traveler toward token theft, or a passkey implementation that trusts the wrong lifecycle step.