[SIGNALS WEEKLY] Hidden Paths: Trusted Tools as Covert Access Channels
Trusted developer projects, cloud services, and stolen secrets are changing the containment problem.
TL;DR
- [Vulnerabilities] Active exploitation of Cisco SD-WAN, FortiMail, Citrix NetScaler, and Zimbra (CVE-2026-73570) is enabling unauthenticated initial access and deep appliance/mail-server compromise at scale.
- [Cyberespionage] State-aligned actors (Star Blizzard, Iran- and China-nexus groups) are refining delivery via trusted infrastructure—compromised websites, developer tooling (Visual Studio projects), DLL sideloading, and legitimate cloud/collaboration services.
- [Defensive Priorities] Traditional patch-and-rebuild is insufficient without identity and secret rotation; defenders should prioritize telemetry on appliance web processes, mail-server child processes, and trusted dev/admin tools that both execute code and reach external services.
Current Stories
TL;DR
- [Vulnerabilities] Cisco, Fortinet, and Citrix products faced confirmed exploitation. NetScaler exposure alone exceeded 50,000 potentially vulnerable internet-facing instances.
- [Email Security] CVE-2026-73570 enabled deep Zimbra compromise. Observed activity included web shells, root escalation, mailbox collection, secret theft, and cluster-wide movement.
- [Cyberespionage] Star Blizzard targeted more than 100 Ukraine-aligned organizations. RedFlick reduced malware installation to one victim interaction and used compromised websites for delivery.
References
- 2026-09-30 Cisco Catalyst SD-WAN Manager API Authentication Bypass Vulnerability
- 2026-10-01 FortiMail Path Traversal Security Advisory
- 2026-09-30 Unauthenticated Command Injection on Internet-Facing Mail Servers
- 2026-09-30 NetScaler Zero Days Exploited in the Wild
- 2026-10-04 CISA Adds One Known Exploited Vulnerability to Catalog
- 2026-09-29 Star Blizzard Refines Phishing and Malware Delivery With RedFlick
Emerging Stories
TL;DR
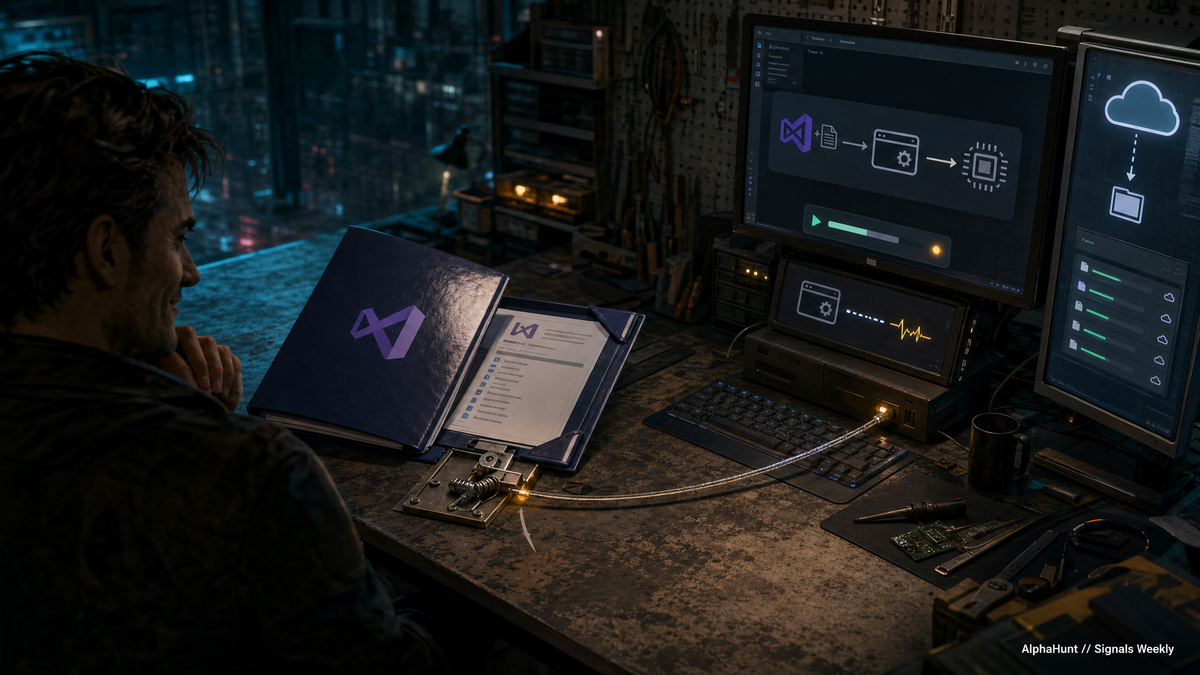
- [Iran-Nexus Activity] Blinder Tunnel turned developer tooling into an entry point. Weaponized Visual Studio projects targeted Iraqi telecommunications, aviation, and critical infrastructure organizations.
- [Risk Prioritization] Disclosure growth is widening the defender filtering problem. Vulnerabilities more than doubled, yet observed exploitation affected only 0.23% of 2026 disclosures.
- [China-Nexus Activity] NeedyMantis enabled durable access across strategic sectors. Victims included telecommunications, universities, government contractors, intergovernmental organizations, and medical nonprofits.
References
- 2026-10-06 Blinder Tunnel Campaign Targets Iraqi Infrastructure
- 2026-09-30 Vulnerability Discovery and Exploitation Trends in the AI Era
- 2026-09-28 NeedyMantis: Unpacking a Post-Compromise Malware Family
Forecasts, Detection Opportunities and References...
Forecasts
TL;DR
- Short-term: State-aligned campaigns will increasingly blend execution and command traffic into trusted software, websites, and cloud platforms.
- Long-term: Identity theft and redundant persistence will make containment harder than initial remediation.
- Overlooked risk: Developer workstations may become preferred bridges into technical teams and downstream production environments.