Vishing Meets Cloud: UNC6040’s Abuse of Salesforce Connected Apps for Stealthy Data Exfiltration
UNC6040 is a financially motivated threat actor specializing in voice phishing (vishing) campaigns that abuse Salesforce Data Loader connected apps to gain unauthorized access and exfiltrate sensitive data. This novel attack vector leverages social engineering via telephone impersonation of...
(Have feedback? Did something resonate with you? Did something annoy you? Just hit reply! :))
Have questions like this:
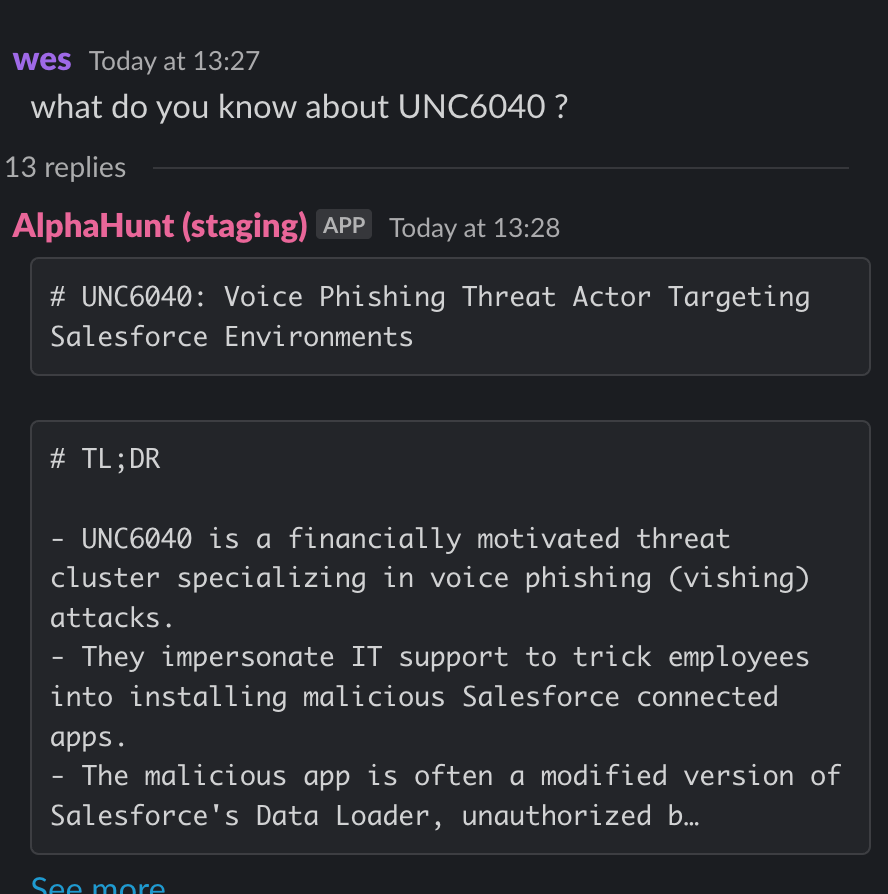
- what do you know about UNC6040 ?
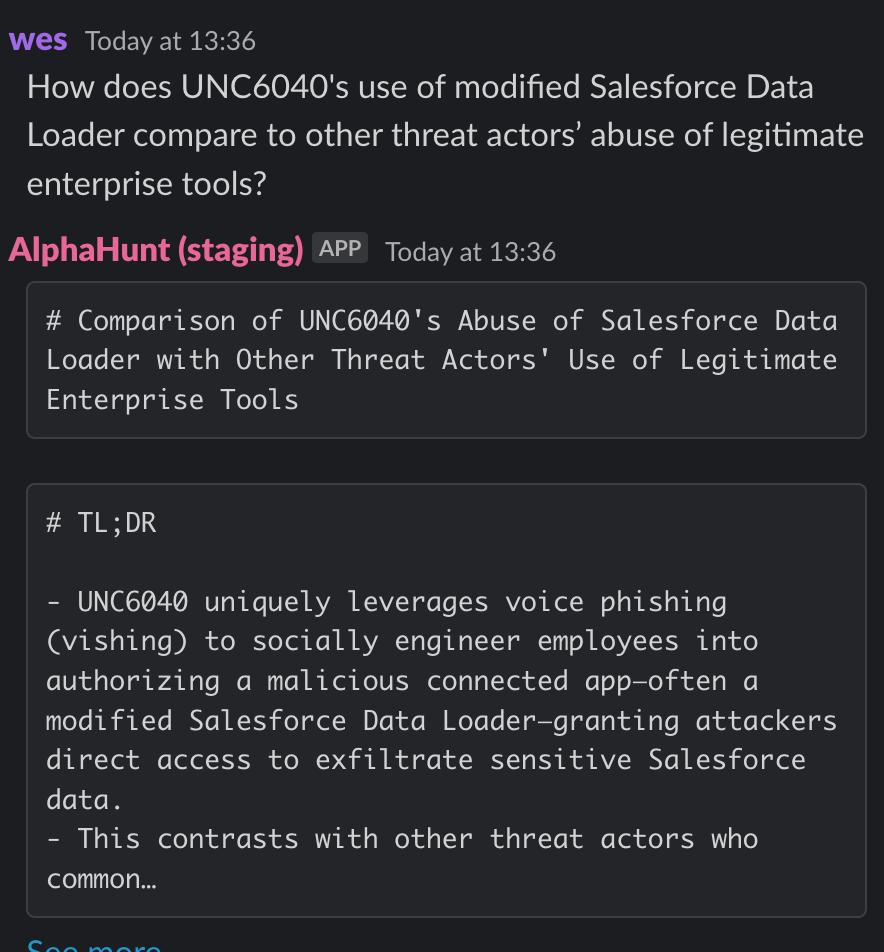
- How does UNC6040's use of modified Salesforce Data Loader compare to other threat actors’ abuse of legitimate enterprise tools?
- How effective are current enterprise security solutions in detecting abuse of legitimate connected apps and remote access tools?
Does it take a chunks out of your day? Would you like help with the research?
This baseline report was thoughtfully researched and took 10 minutes.. It's meant to be a rough draft for you to enhance with the unique insights that make you an invaluable analyst.
We just did the initial grunt work..
Are you ready to level up your skillset? Get Started Here!
Did this help you? Forward it to a friend!
TL;DR
Key Points
-
- UNC6040 leverages voice phishing (vishing) to socially engineer employees into authorizing malicious Salesforce Data Loader connected apps, enabling covert data exfiltration.
- Organizations must enforce strict policy controls, multi-factor authentication (MFA), and continuous monitoring of connected app authorizations to mitigate this attack vector.
-
- The group exploits trusted enterprise tools—including Salesforce which is similar to other actors leveraging ConnectWise and Atera. This complicates detection and response due to the abuse of legitimate credentials and applications.
- Behavioral analytics, user training, and realistic vishing simulations are critical to reducing successful social engineering attacks and improving incident response.
-
- Extortion attempts often follow data theft, with attackers leveraging stolen data months after initial compromise and claiming affiliation with known cybercrime collectives.
- Executive leadership should prioritize risk assessments, incident response planning, and integration of threat intelligence specific to UNC6040 and similar actors.
Executive Summary
UNC6040 is a financially motivated threat actor specializing in voice phishing (vishing) campaigns that abuse Salesforce Data Loader connected apps to gain unauthorized access and exfiltrate sensitive data. This novel attack vector leverages social engineering via telephone impersonation of IT support to trick employees into authorizing malicious connected apps. Similar threat actors abuse legitimate remote access tools such as ConnectWise and Atera by compromising credentials or exploiting misconfigurations. These abuses pose significant organizational and policy risks, including data breaches, compliance violations, financial extortion, and operational disruption. Executive leadership must prioritize policy enforcement, risk management, user training, and technology controls to mitigate these risks effectively.
Research & Attribution
Historical Context
UNC6040 emerged as a distinct financially motivated threat cluster in early 2025, focusing on voice phishing campaigns targeting Salesforce environments. The group manipulates employees into authorizing a modified Salesforce Data Loader connected app, enabling stealthy data exfiltration. UNC6040 has targeted approximately 20 organizations across hospitality, retail, education, and other sectors in the Americas and Europe. The group also moves laterally to cloud services such as Okta, Workplace, and Microsoft 365. Extortion attempts follow data theft, sometimes months later, with attackers claiming affiliation with the ShinyHunters group. UNC6040 shares some infrastructure and tactics with the cybercrime collective "The Com" but remains operationally distinct.
Timeline
- Early 2025: UNC6040 activity identified and reported.
- Mid-2025: Public exposure by Google Cloud and cybersecurity media.
- Ongoing: Targeting of multiple organizations and extortion campaigns.
Origin
UNC6040 is a financially motivated cybercriminal group with no confirmed nation-state ties. It is linked to the broader cybercrime collective "The Com" but is distinct from other groups like UNC3944 (Scattered Spider).
Countries Targeted
- United States – Primary target with multiple sectors affected.
- United Kingdom – Significant targeting in English-speaking markets.
- Canada – Retail and education sectors targeted.
- Germany – European market targeting.
- Australia – Limited targeting reported.
Sectors Targeted
- Hospitality – High-value customer data.
- Retail – Transactional and customer data.
- Education – Sensitive personal and research data.
- Technology – Cloud service access.
- Financial Services – Data theft and extortion.
Motivation
Financial gain through data theft and extortion, leveraging social engineering and abuse of trusted enterprise tools.
Attack Types
- Voice phishing to impersonate IT support.
- Abuse of Salesforce Data Loader connected apps.
- Lateral movement to cloud services.
- Data exfiltration and extortion.
Links to Other APT Groups
- The Com – Loosely organized cybercrime collective sharing infrastructure and tactics with UNC6040.
Similar Threat Actor Groups
- Scattered Spider (UNC3944) – Uses social engineering and targets Salesforce but employs different malware and techniques.
Comparative Analysis and Executive Insights
Organizational and Operational Tactics
UNC6040 uniquely exploits voice phishing to gain authorization for malicious Salesforce connected apps, enabling stealthy data theft. Other threat actors abusing remote access tools like ConnectWise and Atera typically compromise credentials or exploit software vulnerabilities to gain persistent access. Both exploit trusted enterprise tools, complicating detection.
Policy and Governance Challenges
- Over-reliance on trusted enterprise applications without sufficient monitoring.
- Insufficient user training on voice phishing and social engineering.
- Weak policy enforcement on connected app authorizations and remote access tool usage.
- Difficulty detecting abuse of legitimate credentials and tools.
- Governance gaps in cloud access management.
Risks to Enterprise Data Security, Compliance, and Business Continuity
- Data breaches and regulatory violations.
- Financial losses from extortion.
- Reputational damage.
- Operational disruptions.
Strategic Recommendations for Executive Leadership
Policy Enforcement
- Enforce strict approval and MFA for connected app authorizations.
- Apply least privilege and regular access reviews.
- Prohibit unauthorized use of remote access and connected apps.
Risk Management
- Conduct risk assessments focused on social engineering and tool abuse.
- Integrate threat intelligence on UNC6040 and similar actors.
- Develop incident response plans for voice phishing and connected app abuse.
User Training
- Train employees on voice phishing risks.
- Simulate vishing attacks.
- Promote verification culture for IT support requests.
Technology Controls
- Monitor connected app authorizations and remote access tool usage.
- Use behavioral analytics for unusual access patterns.
- Deploy endpoint detection and response tools.
Key Risk Indicators for Executive Oversight
- Increase in voice phishing attempts reported by employees.
- Unauthorized connected app authorizations in Salesforce.
- Anomalous remote access tool usage outside business hours.
- Delays or failures in access review processes.
- Extortion attempts referencing stolen data.
Questions for the Board
- Are policies in place to strictly control connected app authorizations and remote access tools?
- How is user training addressing emerging social engineering threats like voice phishing?
- What monitoring and detection capabilities exist for abuse of legitimate enterprise tools?
- How are incident response plans adapted to address these specific threat vectors?
Recommendations, Actions, Suggested Pivots, Forecasts and Next Steps
(Subscribers Only)
Recommendations, Actions and Next Steps
-
Enforce Strict Policy Controls on Connected App Authorizations and Remote Access Tools with Operational Specificity
- Implement mandatory multi-factor authentication (MFA) and strict approval workflows for all Salesforce connected app authorizations, especially for Data Loader and similar tools. Enforce least privilege access by limiting "API Enabled" and "Manage Connected Apps" permissions to essential administrative personnel only. Conduct automated privilege audits and access reviews quarterly using identity governance tools to detect and revoke unauthorized or excessive permissions. Implement just-in-time (JIT) access for sensitive operations to minimize standing privileges. For remote access tools like ConnectWise and Atera, enforce network segmentation and maintain allow-lists of approved tools and IP ranges, restricting access to trusted enterprise networks only.
- This approach directly mitigates UNC6040’s exploitation of trusted enterprise tools via social engineering and unauthorized app authorizations, significantly reducing the attack surface and preventing stealthy data exfiltration.
- Challenges include integration complexity with existing IAM and network infrastructure, potential user resistance, and the need for ongoing policy enforcement and training.
- Success metrics: Achieve at least a 90% reduction in unauthorized connected app authorizations within six months, maintain quarterly access review compliance above 95%, and zero unauthorized remote access tool usage incidents. These targets align with Salesforce’s security guidance and NIST risk management best practices (NIST SP 800-30).
- MITRE ATT&CK IDs: T1192 (Spearphishing via Service), T1078 (Valid Accounts), T1530 (Data from Cloud Storage Object).
-
Develop and Implement Comprehensive User Training and Realistic Vishing Simulation Programs
- Design and deploy targeted training programs educating employees on voice phishing risks, emphasizing verification protocols for IT support requests. Conduct quarterly simulated vishing exercises with realistic scenarios mimicking UNC6040 tactics, including impersonation of IT support and requests to authorize connected apps. Use training platforms that provide metrics on employee engagement and response accuracy. Promote a verification culture encouraging employees to report suspicious calls immediately.
- This action mitigates the primary attack vector used by UNC6040—voice phishing impersonating IT support—by empowering users to recognize and resist manipulation attempts, reducing successful social engineering breaches.
- Challenges include maintaining engagement and realism in simulations, ensuring training reaches all relevant personnel, and measuring behavioral change over time.
- Metrics for success: Increase employee reporting of suspicious calls by 50% within the first year, reduce successful vishing incidents to near zero, and achieve at least 85% pass rate on post-training assessments. These metrics are supported by Google Cloud’s vishing threat analysis and Salesforce’s social engineering guidance.
- MITRE ATT&CK IDs: T1598 (Phishing: Spearphishing via Service), T1204 (User Execution).
-
Enhance Monitoring, Detection, and Incident Response Capabilities with Behavioral Analytics and Threat Intelligence Integration
- Deploy behavioral analytics and endpoint detection and response (EDR) tools to monitor connected app authorizations and remote access tool usage for anomalous patterns, such as unusual access times, geographic anomalies, or large data exports. Integrate threat intelligence feeds on UNC6040 and related actors to inform detection rules and enrich alerts. Implement Salesforce Shield’s Transaction Security Policies and Event Monitoring to detect and block suspicious Data Loader activities. Develop and regularly update incident response plans specifically addressing voice phishing and connected app abuse scenarios, including tabletop exercises and playbooks.
- This recommendation improves the organization’s ability to detect and respond rapidly to attacks leveraging legitimate tools, minimizing dwell time and the impact of breaches.
- Potential challenges include tuning detection systems to reduce false positives, ensuring adequate staffing and expertise for incident response, and integrating new tools with existing security infrastructure.
- Success metrics: Detect and alert on 95% of anomalous connected app authorizations within 24 hours, reduce incident response time by 30% within six months, and successfully contain 100% of incidents involving connected app abuse in simulated exercises. These align with best practices from Google Cloud and NIST SP 800-30.
- MITRE ATT&CK IDs: T1536 (Credential Access via Cloud Services), T1086 (PowerShell), T1059 (Command and Scripting Interpreter).
Suggested Pivots
-
What specific Salesforce security features—such as Transaction Security Policies, Event Monitoring, API access controls, and connected app approval workflows—are most effective in detecting and preventing unauthorized connected app authorizations exploited by UNC6040, and what gaps remain in current best practices that organizations should address?
-
Which MITRE ATT&CK techniques (e.g., T1536 Credential Access via Cloud Services, T1078 Valid Accounts) and unique indicators of compromise (IOCs) or behavioral patterns characterize UNC6040’s lateral movement within cloud environments like Okta and Microsoft 365, and how can these be distinguished from other threat actors to improve detection and response?
-
What measurable metrics and KPIs—such as reduction in successful vishing incidents, increased employee reporting rates of suspicious calls, and simulation pass rates—have proven effective in evaluating user training and vishing simulation programs, and how can these be tailored to mitigate the specific social engineering tactics employed by UNC6040?
Forecasts
Short-Term Forecast (3-6 months)
UNC6040’s voice phishing campaigns exploiting Salesforce Data Loader connected apps will persist and likely increase in volume and targeting scope, focusing on organizations in the U.S., U.K., Canada, Germany, and Australia across hospitality, retail, education, technology, and financial sectors. The group’s social engineering via telephone impersonation of IT support remains highly effective due to ongoing gaps in user awareness and insufficient enforcement of connected app authorization policies. Organizations without strict multi-factor authentication (MFA) on connected app approvals and lacking behavioral monitoring of remote access tools will face elevated risks of unauthorized access and data exfiltration. Extortion attempts leveraging stolen Salesforce and cloud service data are expected to rise, often delayed by months to maximize impact and complicate response. Executive leadership should prioritize targeted user training with realistic vishing simulations, enforce least privilege access controls, and deploy behavioral analytics to detect anomalous connected app authorizations and remote access tool usage.
Examples
- Google Cloud’s analysis of UNC6040 highlights repeated success in breaching networks via voice phishing and malicious connected app authorization, affecting about 20 organizations since early 2025.
- The Register confirms UNC6040’s effective impersonation of IT support to trick employees into authorizing modified Data Loader apps, enabling stealthy data theft.
- Salesforce’s advisory emphasizes that these attacks exploit user trust and social engineering rather than platform vulnerabilities, underscoring the need for user training and strict app governance.
What to Watch Out For
- Increase in reported voice phishing incidents impersonating IT support within targeted sectors.
- Rise in unauthorized Salesforce connected app authorizations, especially involving Data Loader or similarly privileged apps.
- Detection of anomalous remote access tool usage outside normal business hours or from unusual geolocations.
- Emergence of extortion communications referencing stolen Salesforce or cloud service data.
- Delays or failures in conducting regular access reviews and privilege audits.
- Metrics such as quarterly counts of unauthorized app authorizations and employee reporting rates of suspicious calls.
Long-Term Forecast (12-24 months)
Over the next 12 to 24 months, UNC6040 and similar financially motivated threat actors will likely evolve their social engineering tactics, potentially incorporating emerging technologies such as AI-generated synthetic voices to enhance impersonation credibility. The abuse of trusted enterprise tools will expand beyond Salesforce to other cloud platforms like Okta, Microsoft 365, and Workplace, increasing the attack surface. Organizations that do not adopt zero-trust architectures, continuous behavioral monitoring, and adaptive access controls will remain vulnerable to stealthy data exfiltration and prolonged lateral movement. Regulatory bodies may introduce stricter compliance requirements around connected app governance and social engineering risk management, as indicated by ongoing regulatory focus on cloud security and social engineering mitigation in broader cybersecurity frameworks. Integrated defense strategies combining user training, technology controls, and threat intelligence sharing will become essential to counter these converging threats.
Examples
- UNC6040’s infrastructure overlap with the broader cybercrime collective “The Com” suggests potential sharing of advanced tools and tactics, enabling evolution of attack methods.
- Broader cybersecurity research and industry reports document increasing use of AI-generated deepfake audio in social engineering attacks, indicating a plausible future vector for vishing campaigns.
- Regulatory trends such as GDPR, CCPA, and recent CISA alerts on social engineering indicate growing regulatory attention to cloud app governance and user awareness programs.
What to Watch Out For
- Verified use of AI or synthetic voice technologies in vishing campaigns targeting enterprise users.
- Expansion of attack vectors to include connected apps in cloud services beyond Salesforce.
- Publication or enforcement of new regulatory mandates focused on connected app authorization and social engineering risk mitigation.
- Increased collaboration or convergence between cybercrime collectives sharing infrastructure and tactics.
- Adoption of zero-trust architectures and advanced behavioral analytics by organizations in response to these threats.
- KPIs such as reduction in successful vishing incidents, increased employee reporting rates, and compliance with new regulatory requirements.
MITRE ATT&CK IDs
T1192, T1530, T1078, TA0001, TA0005, TA0010, T1536, T1086, T1059, S0553, S0569, S0570, M1036, M1027, M1047
Appendix
AlphaHunt
(Have feedback? Did something resonate with you? Did something annoy you? Just hit reply! :))
Have questions like this:
- what do you know about UNC6040 ?
- How does UNC6040's use of modified Salesforce Data Loader compare to other threat actors’ abuse of legitimate enterprise tools?
- How effective are current enterprise security solutions in detecting abuse of legitimate connected apps and remote access tools?
Does it take a chunks out of your day? Would you like help with the research?
This baseline report was thoughtfully researched and took 10 minutes.. It's meant to be a rough draft for you to enhance with the unique insights that make you an invaluable analyst.
We just did the initial grunt work..
Are you ready to level up your skillset? Get Started Here!
Did this help you? Forward it to a friend!
(c) 2025 CSIRT Gadgets, LLC
References
- (2025-03-12) Protect Your Salesforce Environment from Social Engineering Threats
- (2025-03-20) Salesforce Security Best Practices: Connected Apps
- (2025-06-04) The Cost of a Call: From Voice Phishing to Data Extortion - Google Cloud Blog
- (2025-06-04) Google Exposes Vishing Group UNC6040 Targeting Salesforce with Fake Data Loader App - The Hacker News
- (2025-06-04) Fake IT support calls hit 20 orgs, end in stolen Salesforce data and extortion, Google warns - The Register
- (2025-07-02) Scattered Spider Threat Actor Profile - Quorum Cyber
- (2024) NIST Special Publication 800-30: Guide for Conducting Risk Assessments
- (2025-05-15) CISA Alert: Avoiding Social Engineering and Phishing Attacks - Cybersecurity and Infrastructure Security Agency
- (2024-12-21) Vishing Threats in 2025: Why Businesses Must Stay Vigilant - Keepnet
MITRE ATT&CK
Techniques
-
T1192 (Spearphishing via Service) – UNC6040 employs voice phishing (vishing) by impersonating IT support personnel to socially engineer employees into authorizing malicious Salesforce connected apps. This is the primary initial access vector, leveraging telephone-based social engineering to bypass technical controls.
-
T1530 (Data from Cloud Storage Object) – UNC6040 exfiltrates sensitive data by abusing authorized Salesforce Data Loader connected apps, extracting data from cloud storage. This technique describes the stealthy data theft method used after gaining access.
-
T1078 (Valid Accounts) – UNC6040 uses valid credentials obtained or authorized through social engineering to move laterally within cloud environments such as Okta, Workplace, and Microsoft 365. This facilitates lateral movement and persistence within cloud services.
Tactics
-
TA0001 (Initial Access) – UNC6040 gains entry by tricking users into authorizing malicious connected apps via voice phishing. This represents the starting point of the attack lifecycle.
-
TA0005 (Defense Evasion) – By abusing legitimate enterprise tools like Salesforce Data Loader and remote access software, UNC6040 evades detection by blending malicious activity with normal operations. This explains how the group avoids triggering security alerts.
-
TA0010 (Exfiltration) – UNC6040 exfiltrates data from cloud storage using authorized connected apps, covering the data theft phase.
Procedures
-
UNC6040 initiates attacks by conducting voice phishing calls impersonating IT support, using scripted social engineering to convince employees to authorize a malicious Salesforce Data Loader connected app. The pretext involves urgent IT support requests requiring app authorization to "resolve system issues," exploiting trust and urgency.
The Cost of a Call: From Voice Phishing to Data Extortion – Google Cloud Blog -
After authorization, UNC6040 registers and deploys a modified Salesforce Data Loader connected app with elevated permissions, enabling stealthy data extraction. The group uses Salesforce’s API and connected app framework to maintain persistence and avoid detection by blending with legitimate app activity.
Salesforce App Hijacked by Hackers: Google Reveals Data Exfiltration Exploit – SalesforceBen -
UNC6040 performs lateral movement within cloud environments such as Okta and Microsoft 365 by leveraging valid accounts obtained through social engineering or credential compromise. The group exploits misconfigurations and weak access controls to escalate privileges and expand access.
Google Exposes Vishing Group UNC6040 Targeting Salesforce with Fake Data Loader App – The Hacker News
Software
- S0591 (ConnectWise) – Remote access tool abused by related threat actors for lateral movement and persistence. Relevant due to similar abuse patterns in the threat landscape.
Mitigations
-
M1036 (User Training) – Conduct targeted training to help users recognize and report voice phishing and social engineering attempts, including simulated vishing exercises. Essential to disrupting UNC6040’s primary attack vector.
-
M1032 (Multi-factor Authentication) – Enforce MFA on connected app authorizations and cloud service access to reduce risk from compromised or socially engineered credentials. Strongly recommended to prevent unauthorized access.
-
M1013 (Application Developer Guidance) – Restrict and monitor connected app authorizations and remote access tool usage, applying least privilege and just-in-time access principles. Helps prevent unauthorized app installations and misuse.
Groups
NONE – UNC6040 is a newly identified financially motivated threat cluster tracked by Google Threat Intelligence Group and is not yet cataloged as a named group in the MITRE ATT&CK framework. Attribution is provisional and subject to refinement as more intelligence emerges. UNC6040 shares some infrastructure and tactics with the loosely organized cybercrime collective "The Com" but remains operationally distinct. It is also separate from the group UNC3944 (Scattered Spider), which targets Salesforce but uses different malware and techniques.
This distinction is important to avoid conflating threat actor profiles and to tailor detection and mitigation strategies appropriately.