[SIGNALS WEEKLY] Edge Intrusions, Cloud Identity Abuse, and Quiet OT Risk
Edge patching may close the hole but not remove access; this issue tracks service-principal abuse and integrator routes into OT.
TL;DR
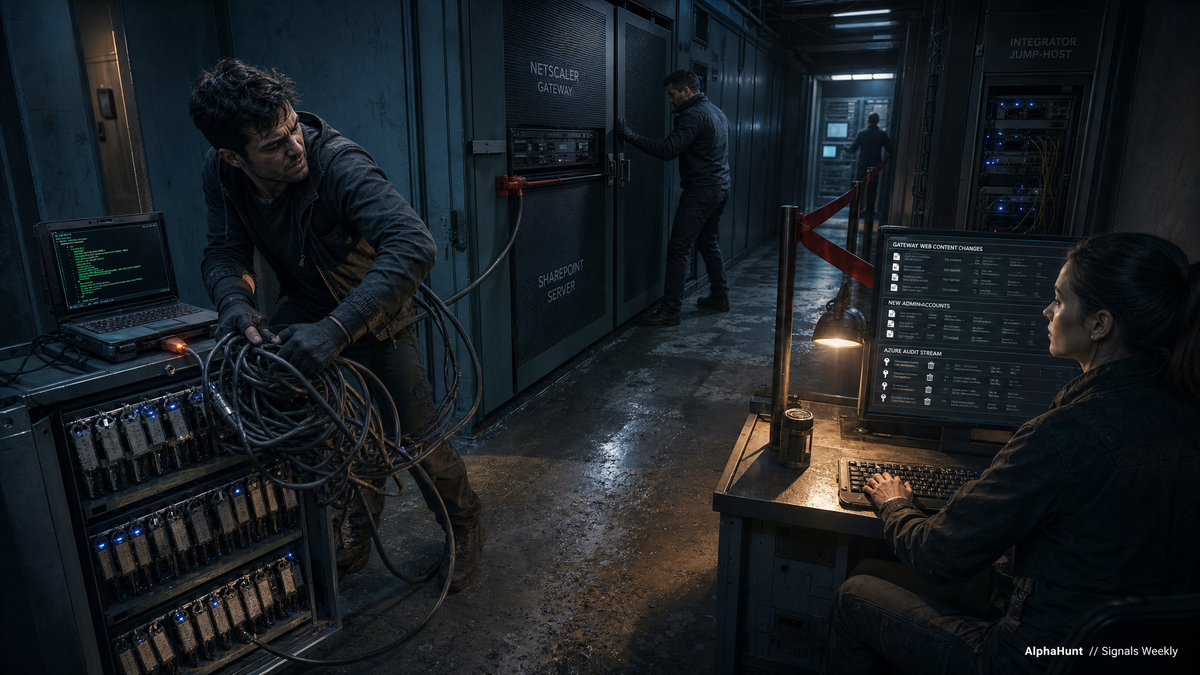
- [Vulnerabilities] Active exploitation of Citrix NetScaler ADC/Gateway (CVE-2026-88771/88772) and SharePoint Server (CVE-2026-65660) enables unauthenticated RCE on internet-edge systems; patching must be paired with webshell, credential, and persistence hunts to avoid “patched-but-owned” outcomes.
- [Cloud / Ransomware] Storm-3168 (JADEPUFFER) leverages compromised Azure service principals for high-speed key theft and destructive control-plane actions, signaling a shift toward identity-led cloud extortion over traditional endpoint encryption.
- [OT / Third-Party Risk] Law-enforcement-driven shutdown guidance for Kiteworks, plus new CISA and NIST OT advisories, highlight growing systemic exposure via managed file transfer platforms and ICS integrators whose remote-access and shared tooling create multi-victim OT compromise paths.
Current Stories
TL;DR
- [Vulnerabilities] Citrix NetScaler ADC/Gateway zero-days (CVE-2026-88771/88772) are being exploited for RCE; prioritize internet-edge patching and compromise checks.
- [Vulnerabilities] CISA added SharePoint Server CVE-2026-65660 to KEV due to active exploitation; remediate any exposed on-prem SharePoint urgently.
- [Cloud / Ransomware] Microsoft observed Storm-3168 (JADEPUFFER) abusing compromised Azure service principals to destroy resources and retrieve keys at speed.
- [Threat Actors / Malware] Microsoft profiled NeedyMantis, a China-aligned modular post-compromise framework used selectively across high-value targets.
References
- (2026-09-28) Critical Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC, Gateway | CISA
- (2026-09-28) Zero-Day Exploitation of Citrix NetScaler ADC and Gateway: CVE-2026-88771 and CVE-2026-88772 | Rapid7
- (2026-09-27) CISA Adds Two Known Exploited Vulnerabilities to Catalog (Citrix CVE-2026-88771/88772) | CISA
- (2026-09-25) CISA Adds Two Known Exploited Vulnerabilities to Catalog (SharePoint CVE-2026-65660) | CISA
- (2026-09-25) Storm-3168: Agentic-driven cloud attacks using compromised service principals | Microsoft
- (2026-09-28) NeedyMantis: Unpacking a post-compromise malware family used in targeted operations | Microsoft
Emerging Stories
TL;DR
- [Managed File Transfer / Pre-exploitation] Kiteworks urged customers to shut down servers based on law-enforcement intel, despite no public CVE or IoCs yet.
- [Supply Chain / OT] FBI+CISA warned that third-party ICS integrators can become high-leverage bridges into OT environments.
- [Standards / OT] NIST published SP 800-82 Rev.4 (IPD), updating OT security guidance with CSF 2.0 and Zero Trust alignment.
References
- (2026-09-25) Kiteworks urges customers to stop using platform after warning from federal intelligence agencies | The Record
- (2026-09-25) Kiteworks urges customers to shut down their servers amid imminent threat of cyberattack | TechCrunch
- (2026-09-23) Considerations for Critical Infrastructure Operators Working With Third-Party ICS Integrators | CISA
- (2026-09-21) Guide to Operational Technology (OT) Security (SP 800-82 Rev. 4 IPD) | NIST CSRC
Top Drivers, Scenarios, Signals and Detection Opportunities
Forecasts
TL;DR
- [from NetScaler/SharePoint] KEV exploitation will evolve quickly into “patched-but-persistently-compromised” incidents as webshells and credentials survive remediation.
- [from Storm-3168] Cloud extortion will increasingly be identity-led, using control-plane deletion/lockout over endpoint encryption.
- [from Kiteworks] More “shutdown-first” advisories are likely when defenders face credible 0-day risk without a disclosed CVE.
- [from ICS integrator guidance] OT compromises will increasingly trace back to integrator remote access and shared tooling, not direct plant-floor exposure.
- [Overlooked] Edit-history and ticketing-system leaks of non-human credentials will continue to fuel repeat access even after user resets.