[SIGNALS WEEKLY] Control Planes Under Pressure: KEV, AI, and Identity
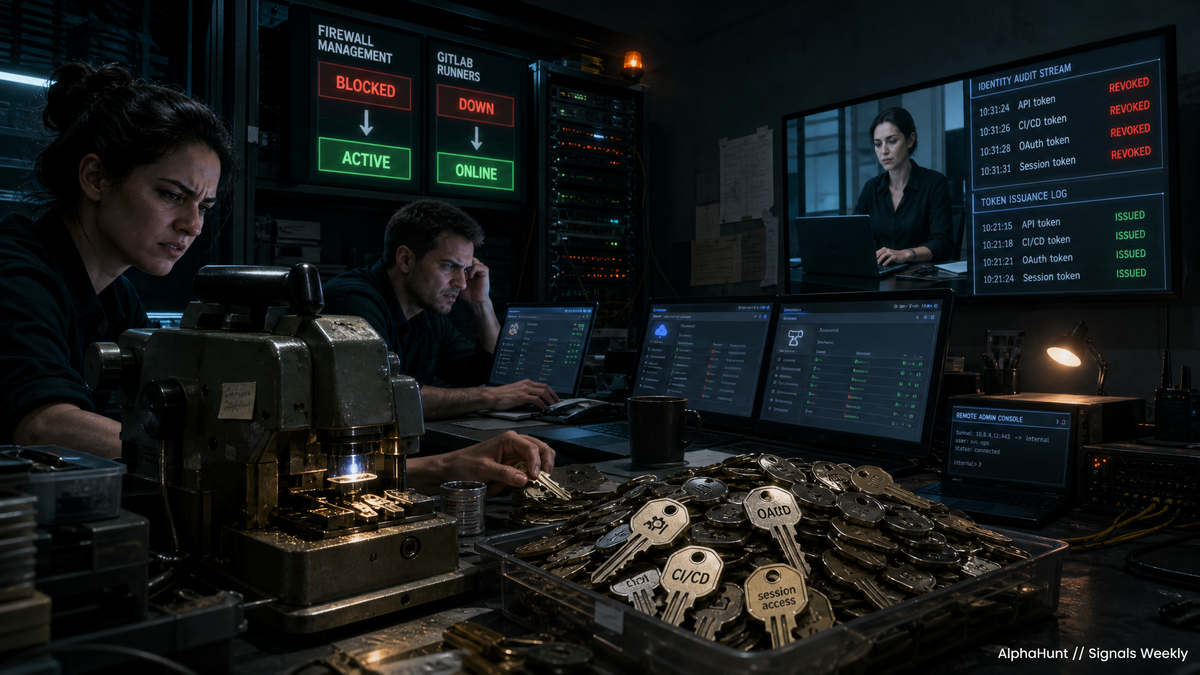
Patch the control plane, then hunt leaked authority: new admins, fresh tokens, API use from new origins. Copied keys can outlive a green patch dashboard.
TL;DR
- [Vulnerabilities] Active exploitation is concentrating on high-leverage control planes (firewall managers, GitLab, remote admin), turning single CVEs into environment-wide compromise risks.
- [Identity/Secrets] The durable risk is post-exploitation credential and secrets theft (tokens, API keys, CI/CD vars), enabling quiet, long-lived re-entry even after patching.
- [AI/Threat Trends] AI-assisted workflows are compressing attacker timelines from recon to lateral movement, making rapid detection and pre-planned secrets rotation critical.
Current Stories
TL;DR
- [Cybercrime/Policy] U.S. action against “Xinbi Guarantee” (Telegram-based illicit marketplace) combines sanctions with DOJ-led seizures and ~$52M crypto restraint, targeting scam-center enabling infrastructure and laundering rails.
- [AI/Threat Trends] Anthropic reports disrupted cases of AI-assisted cyber operations and AI-adjacent credential/token theft, underscoring faster attacker iteration cycles and increased pressure on identity + secrets monitoring.
- [Vulnerabilities] CISA expanded its KEV catalog with multiple actively exploited issues this week, spanning perimeter, remote admin, and developer infrastructure—raising the baseline expectation of broad, opportunistic scanning.
- [Vulnerabilities] Cisco Secure Firewall Management Center (FMC) auth-bypass (CVE-2026-20079) was added to KEV; Talos reports ongoing exploitation against FMC in the wild.
- [Vulnerabilities] GitLab patched a critical unauthenticated path traversal (CVE-2026-85706) enabling arbitrary file read; CISA added it to KEV, increasing urgency for self-managed GitLab estates.
References
- (2026-09-09) Treasury Cracks Down on Transnational Criminal Organization Behind Cyber Scam Operations Targeting Americans
- (2026-09-09) Scam Center Strike Force Conducts Seizures of Chinese-Run Illicit Scammer Marketplace, and Restrains $52 Million in Laundered Crypto Scammer Funds In One Day
- (2026-09-09) Dismantling Transnational Criminal Organization Xinbi Guarantee
- (2026-09-15) Detecting and Countering Misuse of AI: September 2026
- (2026-09-09) CISA Adds Four Known Exploited Vulnerabilities to Catalog
- (2026-09-11) CISA Adds Three Known Exploited Vulnerabilities to Catalog
- (2026-09-11) CISA Adds One Known Exploited Vulnerability to Catalog
- (2026-09-09) Active exploitation of Cisco Secure Firewall Management Center vulnerabilities
- (2026-09-10) GitLab Critical Patch Release: 19.3.2, 19.2.6, 19.1.8
Emerging Stories
TL;DR
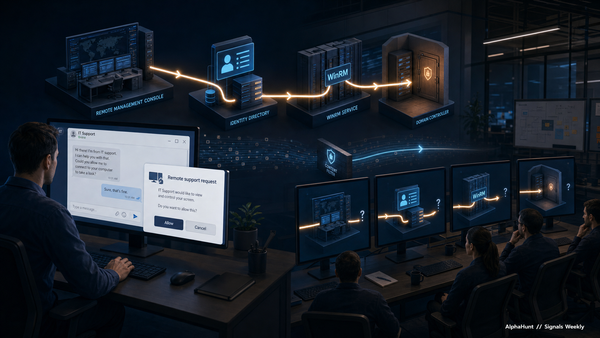
- [Control-Plane Risk] KEV additions are concentrating around “control planes” (management consoles, remote admin, dev tooling). SOC impact this week: one compromise can unlock broad visibility, credentials, and fleet-wide actions—so containment must assume credential/secrets exposure, not just patching.
- [Identity/Secrets] Second-order follow-on is increasingly “secrets spillover” (API keys, CI/CD variables, OAuth/session tokens) rather than repeated CVE re-exploitation. SOC impact: prioritize detections for new token issuance, unusual API use, and rapid credential reuse from new origins.
- [AI/Threat Trends] AI assistance is shifting attacker tradecraft toward shorter OODA loops (faster recon-to-phish, faster exploit adaptation, faster triage). SOC impact: time-to-detect becomes the differentiator; expect more bursty, high-tempo intrusion activity once initial access lands.
References
- (2026-09-15) Detecting and Countering Misuse of AI: September 2026
- (2026-09-09) CISA Adds Four Known Exploited Vulnerabilities to Catalog
- (2026-09-11) CISA Adds Three Known Exploited Vulnerabilities to Catalog
- (2026-09-11) CISA Adds One Known Exploited Vulnerability to Catalog
Forecasts, Detection Opportunities and References...
Forecasts
TL;DR
- Short-term: Expect high-volume exploitation attempts against KEV-listed internet-facing/control-plane services, with rapid credential theft and lateral movement.
- Long-term: Control-plane concentration + AI-accelerated workflows will keep compressing defender response windows; identity and secrets hygiene becomes the primary blast-radius limiter.
- Overlooked risk: “Patch complete, compromise persists” via stolen tokens/keys and new admin accounts created during the initial window.