[GAME THEORY] The Recruiter Was Also the Quartermaster
A new joint advisory links recruiter malware and some DPRK IT workers. Here is where to join hiring, access, and payment decisions.
A developer receives a plausible coding task from a supposed recruiter. A company hires a plausible remote developer and ships a laptop to an address it believes is theirs. Those look like different security problems. A September 18 multinational advisory gives us a reason to examine them together: Japanese police and the FBI assess that WaterPlum—also called Contagious Interview—and some North Korean IT workers operate under the DPRK's 313 General Bureau. It reports that some WaterPlum actors also work as IT workers, and that the groups used the same IP addresses for laptop-farm access, crowdsourcing services, and applications to a Japanese cryptocurrency exchange. [1]
The call: Treat a technical engagement as one cross-functional adversary problem when it can cross trust boundaries—identity, device, source or production access, payment, and monetization. Do not turn every remote hire into an investigation, and do not claim every recruiter lure and fraudulent worker is one campaign. The evidence supports a shared-risk model, not universal operational unity.
The fast read
- The attacker has options. A recruiter lure can compromise a developer's machine and steal sessions, files, or wallet material. A fraudulent worker can acquire legitimate access and salary. A facilitator can supply local laptops, addresses, and payment rails. [1–3]
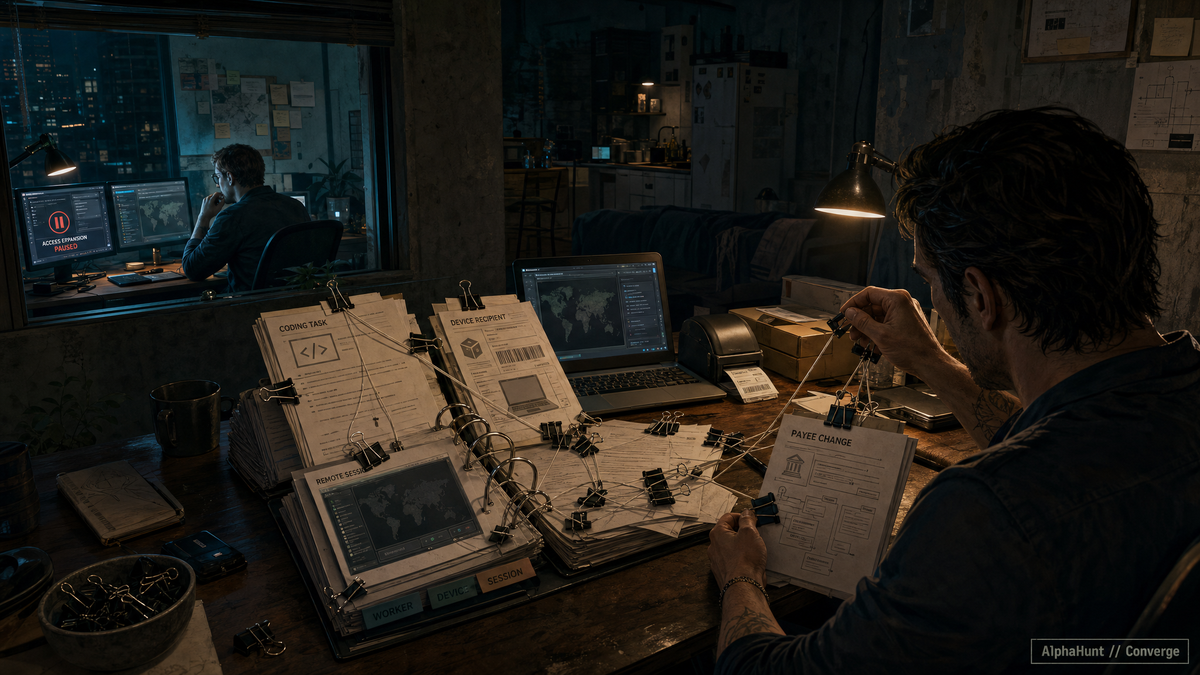
- The defender's weakness is the handoff. HR verifies a name, IT ships a device, engineering grants repository access, and finance pays a beneficiary. Each event may look routine in its own queue.
- The move this week: Pick one high-access contractor engagement and ask whether the named person, device recipient, active session, repository entitlement, and payee can be joined in a single review. If not, name an owner for that join before the next access expansion.
This is not a nationality test. Remote location, VPN use, or a cryptocurrency-payment request alone is not proof of wrongdoing. The question is whether independently observed inconsistencies survive because no one can see the entire relationship.
Below the tear: The useful decision is when to open a joint case, what each owner can constrain, and how to keep the process proportional to the access at stake.
Make the attacker choose a worse route
The principal moves first: decide how hiring, device, access, and payment changes are governed. The adversary then chooses the cheapest route that still pays. Coordinating those decisions does not guarantee detection; it raises the cost of deception and limits what a successful placement or lure can yield.