
gametheory
[GAME THEORY] The Contractor Is Becoming the Intrusion Supply Chain
Integrity Tech’s scanning-to-collection model puts the decision on attack-path ownership, not another attribution desk.
gametheory
Integrity Tech’s scanning-to-collection model puts the decision on attack-path ownership, not another attribution desk.
gametheory
Integrity Tech's capability mix changes the investment question: which routes to mail and identity remain after remediation?
gametheory
Shared intrusion logistics can be a better chokepoint than one APT—if defenders can prove real control-plane dependence.
forecasts
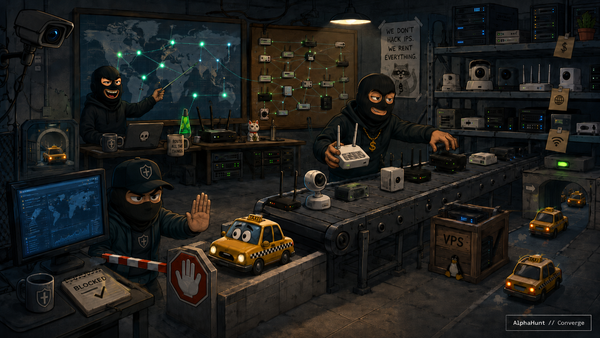
China-linked operators are turning compromised routers into relay logistics. The defender move is behavior over bad IPs.
deep
A bad IP can be accurate and still tell the wrong story.
gametheory
“We patched it” is not an eviction notice. On edge boxes, that sentence has been carrying way too much emotional weight.
forecasts
RedNovember is the kind of crew that turns “it was only an N-day” into a post-incident coping mechanism. We’re at 25% odds they get publicly tied to a true 0-day in 2026. With edge exploitation surging, that’s not exactly comforting. 👀🔥
unc6201
Your backup system isn’t your parachute. It’s a beachhead. 🏖️ Mandiant/GTIG report UNC6201 exploiting Dell RP4VM (CVE-2026-22769, CVSS 10.0). Hardcoded credential → OS-level control + root persistence.
forecasts
Cambodia says it sealed off ~190 scam sites. 🧨 Now the real question: dismantled or displaced? 🧱🚚 Our forecast uses grown-up metrics (convictions + asset denial + independent compound counts).
forecasts
BRICKSTORM intel just landed: PRC actors camping in vCenter/ESXi + Windows. 🧱🕵️♂️ F5 source-code drama raises the long-run 0-day odds, but the calendar + attribution lag are savage. Our final call: 11% UNC5221 gets publicly tied to a new 0-day before Dec 31. 🎯
weekly
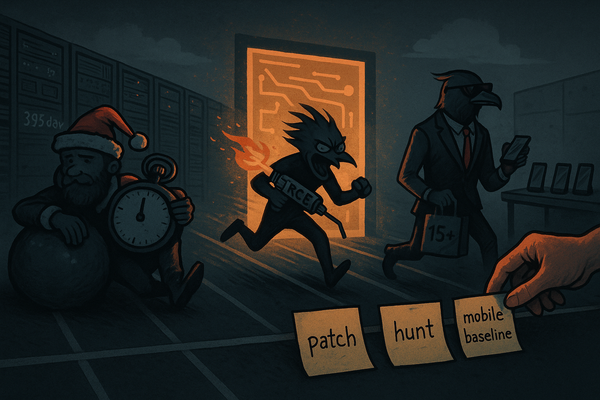
React2Shell in the wild, BRICKSTORM in the walls, Predator on the phone. Not a dystopian haiku—this week’s risk stack. 🧯🕳️📱
china
One “Allow” → tenant-wide weather event. 🌀 AI agent phish wraps the consent flow, device-code keeps churning, and Typhoon rides “good” U.S. infra. Kill list: user consent, device-code, or EWS app perms—what’s first?