weekly
[SIGNALS WEEKLY] Edge Intrusions, Cloud Identity Abuse, and Quiet OT Risk
Edge patching may close the hole but not remove access; this issue tracks service-principal abuse and integrator routes into OT.
weekly
Edge patching may close the hole but not remove access; this issue tracks service-principal abuse and integrator routes into OT.
weekly
The engineer called it internal; the attacker found it internet-adjacent. Inventory and patch exposed GS1900 and Conductor gear, then hunt job changes and secret access.
weekly
Patch the control plane, then hunt leaked authority: new admins, fresh tokens, API use from new origins. Copied keys can outlive a green patch dashboard.
weekly
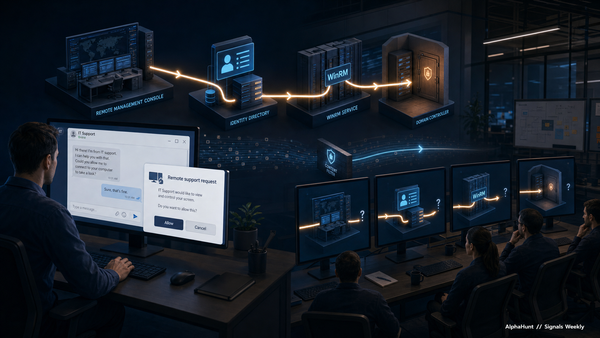
A Teams message from “IT” can now be the first step in a domain takeover: remote-support session, silent install, then AD and WinRM movement.
weekly
Three clocks are running: active PaperCut exploitation, QTFY infrastructure rebuilding after disruption, and AI-agent activity outpacing log governance. Hunt the transitions—not the tidy incident story.

weekly
Exposed management planes are becoming the shortest path from ordinary web access to operational impact. Ray CVE-2025-62593 is now in CISA’s KEV, while new Haiwell and Metasys flaws put AI compute and OT interfaces on the same uncomfortable list.

weekly
Edge exploits, helpdesk vishing, stolen CI tokens, and decentralized C2 share one objective: scale access while shrinking defender visibility. Hunt the transitions, not just the opening IOC.

weekly
Zero-click Zimbra access, exposed PLC tampering, and Teams-to-ransomware chains compress the defender’s window. Prioritize server logs, controller-change evidence, and external admin-surface discovery.

forecasts
We put a 30% chance on two public FCEB cases proving post-deadline edge exploitation by year-end.

weekly
The perimeter kept the keys. Edge appliances and OT switches are becoming the shortest path from exposure to stolen identity and ransomware. The plumbing became the persistence layer.

gametheory
Nine actively exploited flaws show why patching closes an entry point—but not necessarily the incident.

weekly
OAuth consent made SaaS data theft look normal. Niche web plugins kept handing attackers first doors. OT debug ports reminded everyone that “engineering access” can age into exposure.