weekly
[SIGNALS WEEKLY] Edge Compromise, Real-Time Phishing, and Evidence Gaps
Edge-device upgrades do not prove eviction. Preserve evidence, check earlier access, and track real-time phishing beyond the inbox.
weekly
Edge-device upgrades do not prove eviction. Preserve evidence, check earlier access, and track real-time phishing beyond the inbox.
gametheory
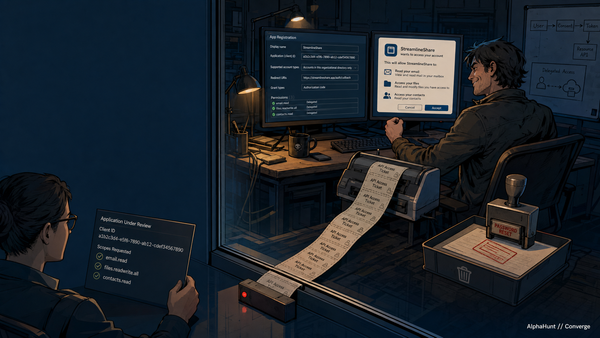
The attacker wants a durable app grant, not a password. Decide who can consent, what needs review, and how you prove revocation.
weekly
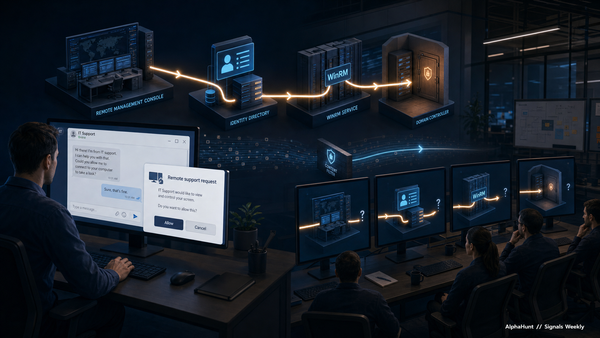
A Teams message from “IT” can now be the first step in a domain takeover: remote-support session, silent install, then AD and WinRM movement.
gametheory
Vishing works because urgency can become SaaS authority. Break the trust transaction without breaking support.
gametheory
Device-code phishing turns a legitimate login flow into rented access. The durable defense is to shrink who can use it.

weekly
The token survived. npm packages, CI/CD runners, and edge boxes keep turning “contained” into “still owned.” The boring weakness became the breach path.

gametheory
The ShinyHunters problem isn’t the name. It’s the chain: MFA reset, weird login, OAuth grant, SaaS export, extortion later.

forecasts
Everyone saw the PLC headline and immediately built their whole Iran take around exposed controllers. Cool. The nastier question is what happens when the next move comes through identity, admin planes, or some target class nobody staffed for.
fraud
“Fraud” makes it sound random. It isn’t. It’s identity infrastructure with a cash-out layer. Same proofing gaps, same rails, same reusable parts. People keep chasing claims instead of the production line.
weekly
Everyone loves “shift left” until the thing in the pipeline shifts your secrets somewhere else. Security tooling has officially joined the attack surface like it was invited.

forecasts
Iran cyber risk is not about whether they’ll be active. They will. The real question is whether the next 8 weeks produce a publicly attributed, materially disruptive hit with a new twist beyond the usual password-spray sludge. Tenant sabotage is the part to watch. 👀🔥

forecasts
Iran cyber risk isn’t just “watch for wipers.” It’s the same ugly identity-first playbook: password sprays, MFA abuse, cloud access… then maybe admin-plane sabotage. Recent reporting says activity is already reaching U.S. targets. Cute.