forecasts
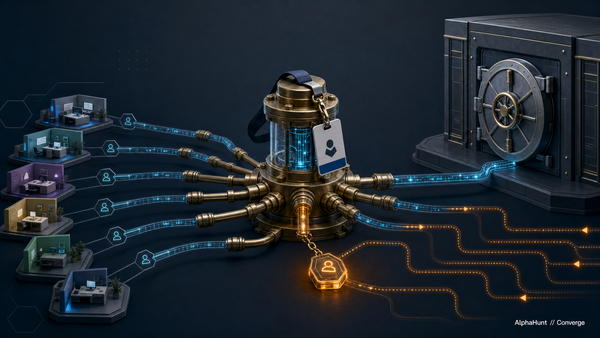
[FORECAST] The SaaS connector is where trust becomes blast radius.
A 30% forecast—and a practical way to reduce the cross-tenant blast radius before the next connector compromise.
forecasts
A 30% forecast—and a practical way to reduce the cross-tenant blast radius before the next connector compromise.

deep
A pod compromise becomes a cloud incident only when workload identity turns execution into transitive authority.

weekly
The login was real. The control plane did the rest. Storm-2949 is the ugly part: one Entra ID identity can turn into SaaS theft and Azure abuse. Nobody owns this until incident day.

forecasts
Everyone saw the PLC headline and immediately built their whole Iran take around exposed controllers. Cool. The nastier question is what happens when the next move comes through identity, admin planes, or some target class nobody staffed for.

forecasts
Iran cyber risk is not about whether they’ll be active. They will. The real question is whether the next 8 weeks produce a publicly attributed, materially disruptive hit with a new twist beyond the usual password-spray sludge. Tenant sabotage is the part to watch. 👀🔥

weekly
Ransomware crews aren’t stopping at endpoints. They’re going after hypervisors, backups, and control planes now. KEV keeps growing, exploitation stays hot, and defender timelines keep getting shorter. Lovely. 🔥💀⚙️
weekly
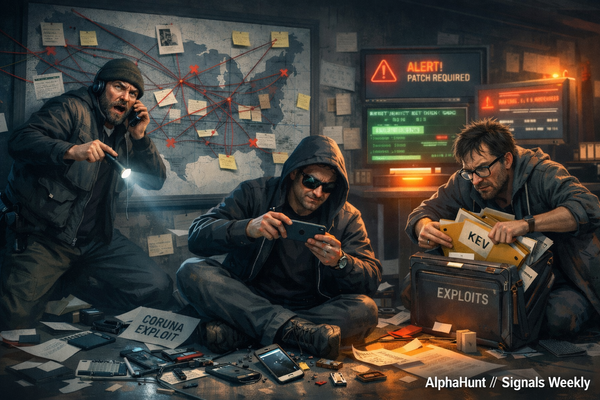
This week’s pattern is ugly and simple: Seedworm is reportedly already sitting inside multiple U.S. organizations, Coruna shows spy-grade iPhone exploitation bleeding into broader use, and KEV + March patch drops are shrinking defender response time from “soon” to “right now.”
weekly
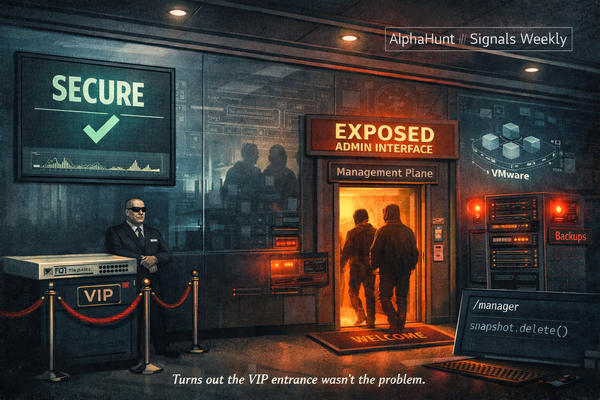
Your firewall isn’t the perimeter. It’s the onboarding portal. 🔥
identity
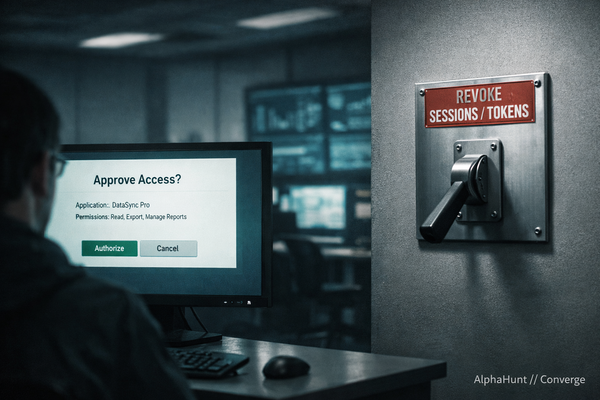
Your SOC isn’t understaffed. It’s late. ⏱️😈 Attackers aren’t scaling with malware—they’re scaling with OAuth + tokens + “normal” API exports. Big tech wins by yanking kill-switches fast. Can you revoke an OAuth grant in <30 min?
weekly
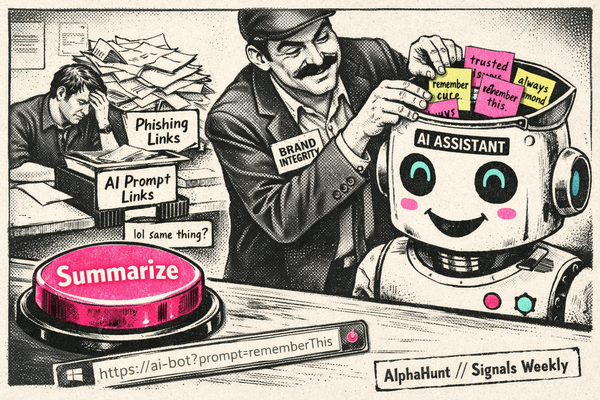
Pre-filled AI prompt links: now a delivery vector. Microsoft warns they can poison assistant recommendations + memory. 🧠🧪
weekly
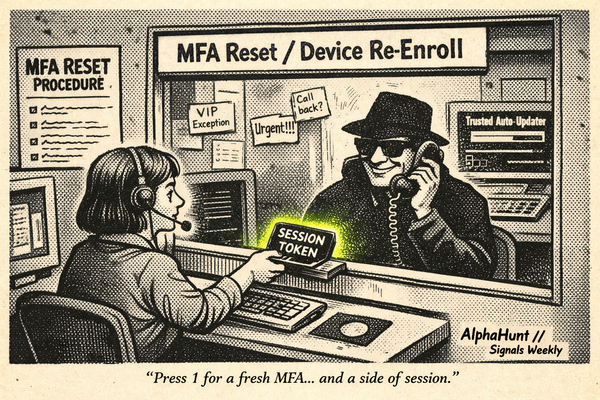
MFA isn’t “done.” It’s now the excuse attackers use on the phone. ☎️😈🔑 Vishing → MFA reset/re-enroll → post-login SaaS data grabs. Plus: selective Notepad++ updater abuse + proxy traffic making IP rep cry.
weekly
🧭 Taiwan CI pressure looks like recon + access maintenance, not a one-off headline. 🩹 Patch Tuesday + KEV = attacker shopping list. ☁️ And Salesforce Aura/Experience Cloud exposure? No patch… just “surprise, it’s public.”