Predatory Sparrow: Pro-Israel Hacktivist Group’s Destructive Cyber Operations Against Iranian Critical Infrastructure
Predatory Sparrow (Gonjeshke Darande) is a pro-Israel hacktivist group, likely state-affiliated, that has escalated destructive cyber operations against Iranian critical infrastructure since the early 2020s. Their attacks—most recently the June 2025 disruption of Bank Sepah—employ ransomware...
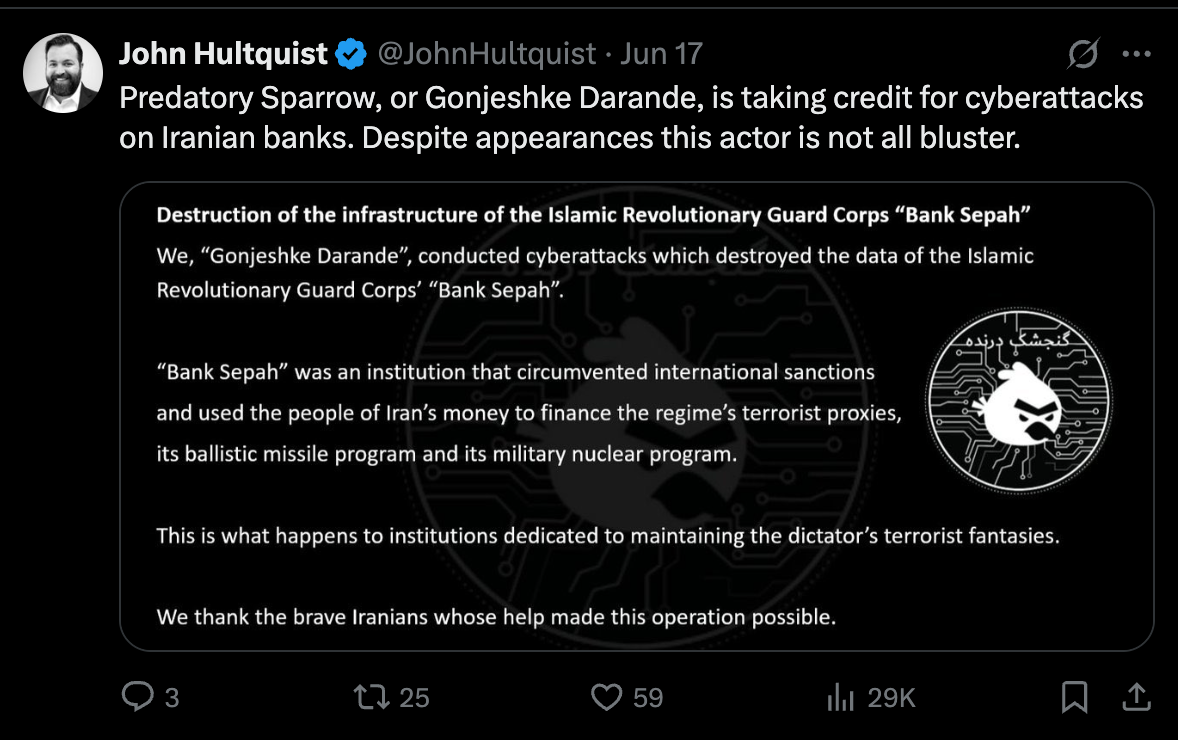
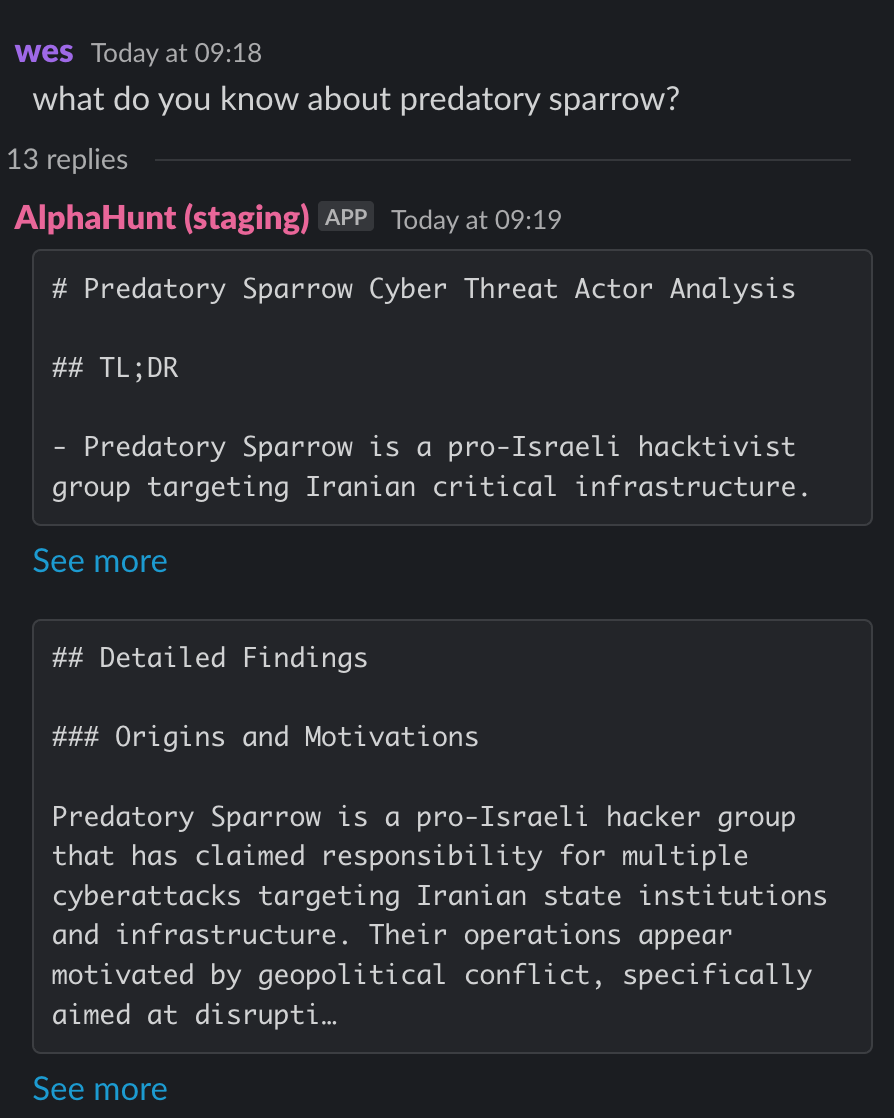
where do i get my ideas??? random social media posts...
(Have feedback? Did something resonate with you? Did something annoy you? Just hit reply! :))
Get questions like this:
- what do you know about predatory sparrow?
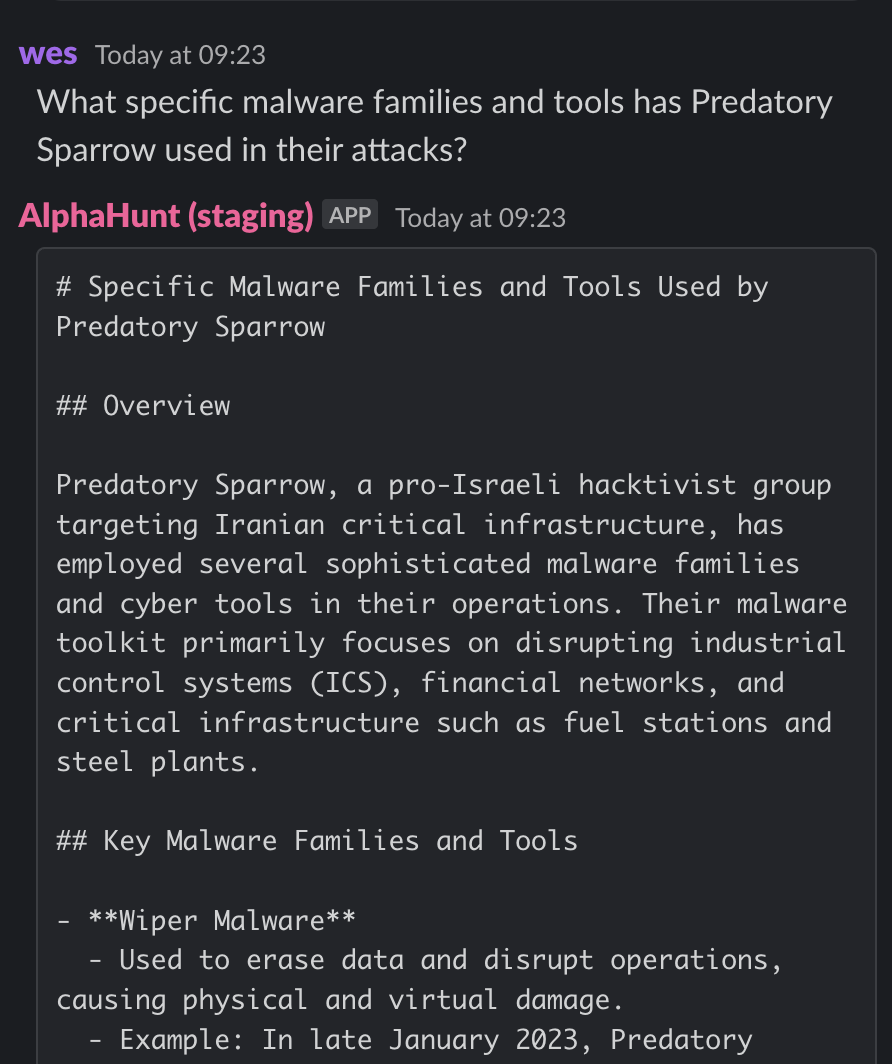
- What specific malware families and tools has Predatory Sparrow used in their attacks?
Does it take a chunks out of your day? Would you like help with the research?
This baseline report was thoughtfully researched and took 10 minutes.. It's meant to be a rough draft for you to enhance with the unique insights that make you an invaluable analyst.
We just did the initial grunt work..
Are you ready to level up your skillset? Get Started Here!
Did this help you? Forward it to a friend!
Suggested Pivot
What specific initial access vectors—such as phishing campaigns, exploitation of known vulnerabilities in Iranian critical infrastructure systems, or supply chain compromises—has Predatory Sparrow likely employed, and how can these be detected or mitigated given the absence of publicly disclosed IOCs?
This question addresses a critical gap in understanding the group’s entry methods, enabling targeted defensive measures and improving early detection capabilities.
TL;DR
Key Points
-
- Predatory Sparrow, a pro-Israel hacktivist group with likely state affiliations, has executed highly disruptive cyberattacks against Iranian critical infrastructure, notably Bank Sepah, using destructive malware and denial-of-service (DoS) tactics.
- Defenders should prioritize advanced EDR with behavioral analytics, network segmentation, and DoS mitigation to counter these sophisticated, multi-vector attacks.
-
- The group’s operations focus on disruption and destruction (not data theft), leveraging ransomware/wiper-like payloads and coordinated DoS, with no public IOCs or malware signatures disclosed.
- Detection and response must rely on behavioral indicators, anomaly detection, and intelligence sharing due to the absence of technical indicators.
-
- Attribution remains circumstantial; Predatory Sparrow is widely believed to be linked to Israeli military intelligence, but no definitive public evidence exists.
- Organizations should monitor for evolving TTPs and anticipate further escalation amid ongoing Israel-Iran tensions.
-
- The group employs psychological operations and public messaging to amplify the impact of attacks, aiming to erode Iranian public morale and influence international perceptions.
- Security teams should integrate cyber threat intelligence (CTI) and counter-influence strategies into their defensive posture.
Executive Summary
Predatory Sparrow (Gonjeshke Darande) is a pro-Israel hacktivist group, likely state-affiliated, that has escalated destructive cyber operations against Iranian critical infrastructure since the early 2020s. Their attacks—most recently the June 2025 disruption of Bank Sepah—employ ransomware/wiper-like malware (MITRE T1486) and coordinated DoS (T1499) to cause operational outages in banking, energy, and industrial sectors. The group’s TTPs include exploitation of network vulnerabilities, possible social engineering, and use of web protocols for command and control (T1071.001), but no specific malware or IOCs have been publicly disclosed, complicating technical attribution and detection.
Predatory Sparrow’s operations are characterized by a focus on disruption and destruction rather than data exfiltration, aligning with strategic objectives to weaken Iranian state capabilities and exert geopolitical pressure. Their public messaging and psychological operations amplify the impact of attacks, contributing to regional instability and shaping adversary perceptions.
Defensive recommendations include deploying advanced EDR with behavioral analytics, enforcing network segmentation and zero trust, implementing robust DoS mitigation, enhancing CTI integration, and conducting targeted social engineering training. Given the group’s operational security and evolving tactics, defenders must rely on behavioral detection, intelligence sharing, and continuous adaptation of security controls.
Forecasts indicate continued escalation of destructive attacks, increased operational security by the group, and further integration of cyber and psychological operations within the broader Israel-Iran conflict. Long-term, the institutionalization of cyber conflict and the evolution of destructive malware—potentially with AI-driven automation—are likely, necessitating ongoing investment in critical infrastructure defense and regional intelligence collaboration.
Research & Attribution
Historical Context
Predatory Sparrow, also known by its Persian name Gonjeshke Darande, is a pro-Israel hacktivist group that gained prominence in the early 2020s for targeting Iranian critical infrastructure. The group has claimed responsibility for cyberattacks disrupting Iranian fuel stations, banking systems, and state-owned industrial facilities. Their activities are part of the broader cyber conflict between Israel and Iran, reflecting escalating digital hostilities that mirror geopolitical tensions in the region. While presenting as hacktivists, Predatory Sparrow is widely believed by cybersecurity experts and intelligence analysts to have links to Israeli military intelligence or state-affiliated actors, though definitive public attribution remains unconfirmed.
Timeline
- Early 2020s: Emergence of Predatory Sparrow with initial attacks on Iranian infrastructure.
- June 2022: Attack on three Iranian state-owned foundries, reportedly causing a fire.
- 2024-2025: Increased cyber operations targeting Iranian fuel stations, rail systems, and banks.
- June 2025: Public claims of a major cyberattack disrupting Bank Sepah, Iran's largest bank, causing outages in banking services and fuel payment systems amid escalating Israel-Iran conflict.
Origin
Predatory Sparrow is attributed to a pro-Israel hacktivist collective, likely linked to Israeli military intelligence or state-sponsored cyber operations. The group uses the Persian name Gonjeshke Darande, indicating a focus on Iranian targets and cultural context. Although Israel does not officially acknowledge offensive cyber operations, multiple high-impact cyber incidents against Iran have been attributed to Israeli state-linked groups, with Predatory Sparrow fitting this pattern. The group’s operational security and selective impact suggest possible legal or strategic constraints governing their activities.
Countries Targeted
- Iran – The primary and almost exclusive target, focusing on critical infrastructure such as banking, energy, and industrial sectors.
Sectors Targeted
- Financial Sector – Attacks on Bank Sepah and other financial institutions to disrupt economic operations and sanctions circumvention.
- Energy Sector – Disruption of fuel stations and related infrastructure to impact energy supply and logistics.
- Industrial Sector – Targeting state-owned foundries and manufacturing facilities linked to Iran’s military and nuclear programs.
Motivation
Predatory Sparrow is motivated by political and ideological objectives aligned with pro-Israel interests. Their operations aim to disrupt Iranian state infrastructure, weaken economic and energy capabilities, and exert pressure on Tehran amid ongoing regional conflicts. The group uses hacktivism as a cover, blending political activism with cyber warfare tactics to achieve strategic impact.
Attack Types
Predatory Sparrow employs a range of destructive and disruptive cyberattack techniques, including:
- Data destruction and encryption (MITRE ATT&CK T1486) to cause operational outages and damage.
- Denial of service attacks (T1499) targeting critical infrastructure endpoints such as fuel stations.
- Use of web protocols for command and control communications (T1071.001).
- Coordinated multi-vector attacks combining disruption of banking services, fuel payment systems, and industrial operations.
- Psychological operations through public claims and messaging to influence perception and morale.
Technical Details and TTPs
- The group has claimed responsibility for attacks that destroyed data belonging to the Islamic Revolutionary Guard Corps' Bank Sepah, causing widespread service outages.
- Attack vectors include exploitation of network vulnerabilities and possibly social engineering to gain initial access, though specific initial access methods remain unconfirmed publicly.
- No specific malware families or custom tools have been definitively attributed to Predatory Sparrow in open-source intelligence or MITRE ATT&CK databases.
- The group’s destructive payloads resemble ransomware or wiper malware, designed to encrypt or erase data to disrupt operations rather than for financial gain.
- Indicators of compromise (IOCs) such as file hashes or command and control infrastructure have not been publicly disclosed.
- Operational tactics include reconnaissance (TA0007), command and control (TA0011), and impact (TA0040) phases, consistent with sophisticated cyber operations targeting critical infrastructure.
Known Aliases
- Predatory Sparrow (Google Threat Intelligence Group)
- Gonjeshke Darande (Persian name used by the group and recognized by analysts)
Key Takeaways
- Predatory Sparrow is a pro-Israel hacktivist group targeting Iranian critical infrastructure, especially banking and energy sectors.
- The group uses destructive cyberattacks to disrupt services, including data destruction and denial of service.
- While publicly presenting as hacktivists, they are widely believed to have state affiliations, likely linked to Israeli military intelligence.
- Their attacks have caused significant operational outages, including a major disruption of Bank Sepah in June 2025.
- No specific malware or IOCs have been publicly disclosed, but their tactics align with sophisticated cyber warfare operations.
- Attribution remains circumstantial, with no definitive public evidence linking them to a specific government entity.
Recommendations, Actions, Suggested Pivots, Forecasts and Next Steps
(Subscribers Only)
Recommendations, Actions, and Next Steps
Predatory Sparrow, a pro-Israel hacktivist group with likely state affiliations, has recently executed highly disruptive cyberattacks against Iranian critical infrastructure, notably causing major outages at Bank Sepah in June 2025. These attacks leverage destructive malware and denial-of-service tactics to impair financial, energy, and industrial sectors. The following prioritized recommendations are tailored to counter the group’s sophisticated tactics and mitigate operational impacts.
-
Implement Advanced Endpoint Detection and Response (EDR) with Behavioral Analytics for Ransomware and Wiper Malware
- Deploy EDR solutions that monitor for behaviors indicative of destructive payloads, such as mass file encryption, deletion of shadow copies, unauthorized use of administrative tools (e.g., PowerShell, WMIC), and rapid file renaming or wiping activities.
- Integrate these tools with Security Information and Event Management (SIEM) systems to enable real-time alerts and automated containment.
- This directly counters Predatory Sparrow’s use of data destruction (MITRE ATT&CK T1486) and reduces downtime by enabling rapid detection and response.
- Implementation requires selecting EDR platforms with proven ransomware detection capabilities, training SOC analysts on behavioral indicators, and establishing incident response playbooks aligned with NIST SP 800-61 guidelines.
- Challenges include tuning detection to minimize false positives and ensuring continuous updates to threat signatures.
- Metrics: Reduction in time to detect ransomware/wiper activity, number of prevented destructive events, and incident response times.
- MITRE ATT&CK IDs: T1486 (Data Encrypted for Impact), T1059 (Command and Scripting Interpreter).
-
Strengthen Network Segmentation and Zero Trust Access Controls for Critical Infrastructure Systems
- Architect network segmentation to isolate critical assets (banking systems, fuel station networks, industrial control systems) from corporate and public networks.
- Enforce Zero Trust principles by requiring continuous verification of user and device identities, implementing multi-factor authentication (MFA), and least privilege access.
- This limits initial access vectors and lateral movement exploited by Predatory Sparrow, which likely uses network vulnerabilities and social engineering.
- Steps include network mapping, deploying micro-segmentation technologies, and integrating identity-aware proxies or software-defined perimeters.
- Challenges include operational complexity and potential disruptions during deployment.
- Metrics: Number of unauthorized access attempts blocked, audit compliance rates, and reduction in lateral movement incidents.
- MITRE ATT&CK IDs: T1078 (Valid Accounts), T1071.001 (Web Protocols - Command and Control).
-
Deploy Comprehensive Denial of Service (DoS) Mitigation Solutions Including Cloud-Based Scrubbing and Rate Limiting
- Implement multi-layered DoS protection combining on-premises appliances, cloud-based scrubbing services, and ISP-level filtering to protect critical endpoints such as fuel stations and banking services.
- Use anomaly detection systems to identify and block volumetric and application-layer DoS attacks (MITRE ATT&CK T1499).
- Follow ENISA and NIST best practices for DoS mitigation, including regular stress testing and incident response planning.
- Challenges include cost of advanced mitigation services and balancing protection with legitimate traffic flow.
- Metrics: Service uptime during attack attempts, volume of malicious traffic mitigated, and time to restore services.
- MITRE ATT&CK IDs: T1499 (Endpoint Denial of Service).
-
Enhance Cyber Threat Intelligence (CTI) Integration and Sharing with Regional and International Partners
- Establish formal CTI sharing agreements with government agencies (e.g., CISA), industry ISACs, and trusted vendors to receive timely updates on emerging TTPs, IOCs, and vulnerabilities related to Predatory Sparrow and similar actors.
- Integrate CTI feeds into security tools for automated detection and response.
- This addresses the current lack of publicly available IOCs and enables proactive defense.
- Implementation involves subscribing to reputable CTI sources, configuring automated ingestion pipelines, and training analysts on intelligence use.
- Metrics: Number of actionable intelligence alerts received, time to incorporate intelligence into defenses, and reduction in successful intrusions.
- MITRE ATT&CK IDs: TA0007 (Reconnaissance), TA0011 (Command and Control).
-
Conduct Targeted Cybersecurity Awareness and Social Engineering Training Focused on Critical Infrastructure Personnel
- Develop and deliver training programs emphasizing recognition of phishing, spear-phishing, and other social engineering tactics that may be used to gain initial access.
- Conduct regular simulated phishing campaigns and reinforce reporting mechanisms.
- This mitigates the likely initial access vector used by Predatory Sparrow.
- Challenges include maintaining engagement and measuring effectiveness.
- Metrics: Phishing click rates, incident reporting frequency, and reduction in successful social engineering incidents.
- MITRE ATT&CK IDs: T1566 (Phishing).
Suggested Pivots
-
What specific initial access vectors—such as phishing campaigns, exploitation of known vulnerabilities in Iranian critical infrastructure systems, or supply chain compromises—has Predatory Sparrow likely employed, and how can these be detected or mitigated given the absence of publicly disclosed IOCs?
This question addresses a critical gap in understanding the group’s entry methods, enabling targeted defensive measures and improving early detection capabilities. -
How do Predatory Sparrow’s operational security measures and selective targeting reflect possible legal, strategic, or political constraints imposed by their suspected state affiliations, and what predictive indicators can be derived to anticipate future attack timing, scope, or escalation?
Understanding these constraints can help forecast the group’s behavior and inform strategic risk assessments for Iranian and regional infrastructure. -
What are the broader geopolitical and regional stability implications of Predatory Sparrow’s disruptive cyberattacks on Iran’s banking and energy sectors, particularly in the context of escalating Israel-Iran tensions and potential retaliatory cyber or kinetic responses?
This pivot explores the cascading effects of cyber operations on international security and conflict dynamics, informing policy and diplomatic considerations. -
What concrete mechanisms—such as participation in Information Sharing and Analysis Centers (ISACs), establishment of joint cyber task forces, or deployment of automated threat intelligence platforms—can be implemented or enhanced to improve real-time intelligence sharing and coordinated defense against Predatory Sparrow’s multi-vector cyber operations?
Focusing on actionable collaboration frameworks will strengthen collective defense and reduce response times to emerging threats. -
How does Predatory Sparrow employ psychological operations and information warfare through their public claims and messaging, and what impact do these tactics have on Iranian public morale, adversary decision-making, and international perceptions of the cyber conflict?
Analyzing these influence operations can guide counter-propaganda efforts and strategic communications to mitigate adversary advantages.
Forecast
Short-Term Forecast (3-6 months)
-
Escalation of Disruptive Cyberattacks on Iranian Critical Infrastructure by Predatory Sparrow
- Predatory Sparrow is expected to intensify destructive cyber operations targeting Iranian banking, energy, and industrial sectors, leveraging ransomware- or wiper-like malware (T1486) and denial-of-service attacks (T1499) to cause operational outages. The June 2025 Bank Sepah disruption exemplifies this escalation amid heightened Israel-Iran tensions.
- Similar to the Shamoon attacks on Saudi Aramco in 2012, these operations aim to inflict maximum disruption without data theft, focusing on economic and logistical paralysis.
- What to watch for:
- New public claims or evidence of attacks on additional Iranian banks or energy infrastructure
- Increased frequency or scale of denial-of-service incidents targeting critical endpoints
- Emergence of new destructive malware variants or attack vectors linked to the group
-
Iranian Defensive Enhancements Focused on Behavioral EDR and Network Segmentation
- Iranian critical infrastructure operators will likely accelerate deployment of advanced endpoint detection and response (EDR) solutions with behavioral analytics tailored to detect ransomware and wiper malware behaviors (e.g., mass file encryption, shadow copy deletion).
- Network segmentation and zero trust access controls will be prioritized to limit lateral movement (T1078) and contain breaches, reflecting lessons from prior Shamoon and NotPetya incidents.
- Recent Iranian government cybersecurity initiatives, such as increased investment in domestic cyber defense capabilities and partnerships with regional allies, support this forecast.
- What to watch for:
- Public announcements or intelligence reports of Iranian adoption of specific EDR platforms or zero trust frameworks
- Reduction in successful lateral movement or ransomware incidents reported in Iranian infrastructure
-
Continued Operational Security and Ambiguity in Attribution by Predatory Sparrow
- The group will maintain strict operational security, avoiding public disclosure of IOCs and malware signatures to preserve plausible deniability and complicate attribution efforts.
- This will necessitate reliance on behavioral detection and anomaly-based defenses by Iranian and allied cybersecurity teams.
- What to watch for:
- Persistent absence of detailed technical indicators in open-source intelligence
- Increased emphasis on behavioral analytics in cybersecurity defenses targeting Iranian infrastructure
-
Expansion of Psychological Operations and Influence Campaigns
- Predatory Sparrow will likely increase use of public claims and messaging to influence Iranian public morale and international perceptions, integrating cyberattacks with information warfare.
- This mirrors tactics used by groups like APT33 and Shamoon operators, who combined cyber disruption with psychological impact.
- What to watch for:
- Coordinated messaging campaigns on social media or state media platforms following cyber incidents
- Increased cyber-enabled influence operations linked to the group or its affiliates
-
Adoption of Multi-Vector Attack Coordination and Sophisticated C2 Techniques
- The group will refine multi-vector attacks combining data destruction, denial-of-service, and command and control via web protocols (T1071.001) to enhance stealth and resilience.
- This approach complicates incident response and mirrors advanced persistent threat (APT) behaviors seen in state-sponsored campaigns.
- What to watch for:
- Reports of simultaneous outages across multiple Iranian critical infrastructure sectors
- Indicators of complex attack chains and long dwell times in compromised networks
Long-Term Forecast (12-24 months)
-
Institutionalization of Cyber Conflict as a Persistent Israel-Iran Rivalry Element
- Cyber operations by Predatory Sparrow or affiliated pro-Israel groups will become a normalized, ongoing facet of the Israel-Iran conflict, with periodic escalations linked to geopolitical events.
- Historical parallels include the sustained cyber campaigns by Iranian APTs against Israeli infrastructure, suggesting a cyclical pattern of retaliation and escalation.
- What to watch for:
- Cyclical spikes in cyberattacks correlating with diplomatic or military tensions
- Emergence of new pro-Israel cyber groups adopting similar TTPs
-
Evolution of Destructive Malware and Integration of AI-Driven Automation
- Destructive malware capabilities will advance, incorporating sophisticated evasion, persistence, and possibly AI-driven automation for attack orchestration and adaptive targeting.
- This evolution will increase the speed and scale of attacks, potentially enabling real-time adaptation to defensive measures.
- What to watch for:
- Discovery of new malware variants with advanced stealth or autonomous capabilities
- Reports of cyber-physical incidents linked to the group’s operations
-
Expansion of Targeting to Iranian Proxies and Regional Infrastructure
- Predatory Sparrow may broaden its targeting to Iranian proxies (e.g., Hezbollah) and critical infrastructure supporting Iran’s regional influence, aiming to disrupt supply chains and allied operations indirectly.
- This mirrors tactics used by other state-linked groups targeting proxy networks to extend strategic impact.
- What to watch for:
- Intelligence reports of attacks on non-Iranian entities linked to Iranian strategic interests
- Increased regional cyber incidents with similar TTP signatures
-
Regional Cyber Defense Institutionalization and Intelligence Sharing Enhancements
- Iran and regional actors will likely formalize cyber defense capabilities, establishing joint cyber task forces, ISACs, and automated threat intelligence sharing platforms to counter multi-vector cyber operations.
- This will improve detection, response, and resilience, reflecting global trends in critical infrastructure protection.
- What to watch for:
- Announcements of regional cyber defense initiatives or intelligence sharing agreements
- Increased public-private collaboration on cybersecurity in the Middle East
-
Integration of Cyber Psychological Operations with Kinetic and Diplomatic Actions
- Psychological operations via cyber means will become more integrated with kinetic military actions and diplomatic efforts, using cyberattacks and messaging to shape adversary decision-making and public opinion.
- Predatory Sparrow’s public claims and messaging will evolve into coordinated influence campaigns supporting broader strategic objectives.
- What to watch for:
- Evidence of synchronized cyber and information campaigns timed with geopolitical events
- Increased sophistication in adversary influence operations leveraging cyber incidents
MITRE ATT&CK IDs
- T1486 (Data Encrypted for Impact) – Destructive malware encrypting or wiping data to disrupt Iranian infrastructure
- T1499 (Endpoint Denial of Service) – DoS attacks targeting fuel stations and banking services
- T1071.001 (Web Protocols – Command and Control) – Use of web protocols for stealthy C2 communications
- T1059 (Command and Scripting Interpreter) – Use of scripting for payload execution and lateral movement
- T1078 (Valid Accounts) – Use of legitimate credentials for persistence and lateral movement
- T1566 (Phishing) – Likely initial access vector via phishing or spear-phishing
- T1083 (File and Directory Discovery) – Reconnaissance to identify critical data for destruction
- T1204 (User Execution) – Reliance on user execution of malicious files or links
- TA0040 (Impact) – Techniques aimed at disrupting system availability and integrity
- TA0011 (Command and Control) – Maintaining communication with compromised systems
- TA0007 (Discovery) – System and network reconnaissance
- TA0006 (Credential Access) – Obtaining credentials for persistence
- TA0001 (Initial Access) – Gaining initial foothold in target networks
Appendix
References
- (2025-06-17) - Iran-Israel Conflict Spills to Digital World, Inflaming Rivalry - Bloomberg
- (2025-06-17) - FDD Analysis: Israel Targets IRGC General and Disrupts Iranian Banks
- (2025-06-04) - CISA Updated Guidance on Play Ransomware
- (2025-03) - ENISA Threat Landscape Report 2024
- (2024-10-25) - Iran's Cybersecurity Threatscape for 2021-H1 2024 - PT Security
- (2025-06-17) - Iran’s Bank Sepah disrupted by cyberattack claimed by pro-Israel hacktivist group - CyberScoop
- (2025-06-17) - Pro-Israel Hacking Group Claims to Disrupt Iran's Bank Sepah
- (2025-06-17) - Pro-Israel hackers claim breach of Iranian bank amid military escalation
AlphaHunt
(Have feedback? Did something resonate with you? Did something annoy you? Just hit reply! :))
Get questions like this:
- what do you know about predatory sparrow?
- What specific malware families and tools has Predatory Sparrow used in their attacks?
Does it take a chunks out of your day? Would you like help with the research?
This baseline report was thoughtfully researched and took 10 minutes.. It's meant to be a rough draft for you to enhance with the unique insights that make you an invaluable analyst.
We just did the initial grunt work..
Are you ready to level up your skillset? Get Started Here!
Did this help you? Forward it to a friend!
(c) 2025 CSIRT Gadgets, LLC
MITRE ATT&CK
Techniques
-
T1486 (Data Encrypted for Impact) – The group deploys destructive malware that encrypts or wipes data, causing operational outages and damage to Iranian critical infrastructure such as Bank Sepah.
- This technique is central to Predatory Sparrow’s disruptive cyberattacks, reflecting their use of ransomware- or wiper-like payloads to inflict damage rather than financial gain.
- Data Encrypted for Impact
- CISA Updated Guidance on Play Ransomware
- Bloomberg: Pro-Israel Hackers Claim Cyberattack on Iran
-
T1499 (Endpoint Denial of Service) – Execution of denial-of-service attacks targeting critical infrastructure endpoints such as fuel stations and banking services.
- Predatory Sparrow’s multi-vector attacks include DoS to disrupt availability of Iranian energy and financial systems.
- Endpoint Denial of Service
- ENISA Threat Landscape Report 2024
-
T1071.001 (Web Protocols – Command and Control) – Use of web protocols for command and control communications to maintain stealthy and resilient control over compromised systems.
- This technique supports the group’s operational security and remote coordination of attacks.
- Web Protocols
-
T1059 (Command and Scripting Interpreter) – Use of scripting languages and command interpreters (e.g., PowerShell) to execute malicious commands and deploy destructive payloads.
- Enables flexible execution of destructive actions and lateral movement within networks.
- Command and Scripting Interpreter
-
T1078 (Valid Accounts) – Use of stolen or legitimate credentials to gain and maintain access, facilitating lateral movement and persistence.
- Likely employed to navigate Iranian networks and avoid detection.
- Valid Accounts
-
T1566 (Phishing) – Use of phishing or spear-phishing to gain initial access.
- While initial access vectors remain unconfirmed, phishing is a common and plausible method.
- Phishing
-
T1083 (File and Directory Discovery) – Discovery of files and directories to identify critical data for destruction.
- Supports targeted destructive operations by identifying valuable or sensitive files.
- File and Directory Discovery
-
T1204 (User Execution) – Reliance on user execution of malicious files or links to initiate compromise.
- Relevant to social engineering tactics potentially used by the group.
- User Execution
Tactics
-
TA0040 (Impact) – Techniques aimed at disrupting availability or compromising integrity of systems.
- Predatory Sparrow’s primary objective is to cause operational disruption and damage to Iranian critical infrastructure.
- Impact
- FDD Analysis: Israel Targets IRGC General and Disrupts Iranian Banks
-
TA0011 (Command and Control) – Establishing and maintaining communication with compromised systems.
- Essential for coordinating multi-vector attacks and maintaining operational control.
- Command and Control
-
TA0007 (Discovery) – Gathering information about systems and networks to identify targets.
- Enables precise targeting of critical infrastructure components.
- Discovery
-
TA0006 (Credential Access) – Techniques to obtain credentials for persistence and lateral movement.
- Supports stealthy access and control within target networks.
- Credential Access
-
TA0001 (Initial Access) – Gaining initial foothold in the target environment.
- Critical phase, though specific vectors remain unconfirmed.
- Initial Access
Procedures
-
Destructive Malware Deployment
- Predatory Sparrow deploys ransomware- or wiper-like malware that encrypts or erases data on Iranian critical infrastructure systems, causing outages such as those at Bank Sepah. The malware behavior includes mass file encryption, deletion of backups, and disabling recovery mechanisms, consistent with tactics described in CISA’s ransomware guidance.
- CISA Updated Guidance on Play Ransomware
- Bloomberg Report on Bank Sepah Attack
-
Coordinated Denial of Service Attacks on Critical Infrastructure
- The group conducts multi-vector DoS attacks targeting endpoints such as fuel stations and banking services, leveraging volumetric and application-layer techniques to overwhelm systems and disrupt availability.
- ENISA Threat Landscape Report 2024
-
Command and Control via Web Protocols
- Use of HTTP/HTTPS and other web protocols for C2 communications to evade detection and maintain persistent control over compromised hosts.
- MITRE ATT&CK Web Protocols
-
Use of Valid Credentials and Lateral Movement
- Exploitation of valid accounts to move laterally within networks, escalate privileges, and maintain persistence, consistent with observed credential access and use patterns.
- MITRE ATT&CK Valid Accounts
Mitigations
-
M1059 (Data Backup) – Maintain regular, secure backups of critical data to enable recovery from destructive attacks.
- Essential to mitigate the impact of data encryption and wiping.
- Data Backup
- CISA Ransomware Guidance
-
M1036 (Account Use Policies) – Enforce strict account use policies, including monitoring and limiting privileged account usage.
- Helps prevent misuse of valid accounts for lateral movement.
- Account Use Policies
-
M1037 (Network Segmentation) – Segment networks to isolate critical infrastructure and limit lateral movement.
- Reduces attack surface and confines potential breaches.
- Network Segmentation
-
M1047 (Phishing Protection) – Implement user training and technical controls to reduce phishing success.
- Mitigates likely initial access vectors.
- Phishing Protection
-
M1039 (Denial of Service Protection) – Deploy multi-layered DoS mitigation including cloud scrubbing and rate limiting.
- Protects critical endpoints from DoS attacks.
- Denial of Service Protection
- ENISA DoS Mitigation Best Practices