Hypervisor Ransomware: CVE-2024-37085, AD Abuse, and the Escalating Threat to VMware ESXi Environments
Ransomware groups—including BlackCat/ALPHV, Black Basta, RansomHub, and Dark Angels—are increasingly targeting VMware ESXi and similar virtualization platforms using advanced hypervisor-level attack techniques. The exploitation of CVE-2024-37085..
(Have feedback? Did something resonate with you? Did something annoy you? Just hit reply! :))
Have a ESXi Environment- not sure what these headlines mean??
- Scattered Spider (UNC3944) is conducting a VMware ESXi hacking spree, leveraging social engineering to gain privileged access and deploy ransomware in U.S. airline, retail, transportation, and insurance sectors ?
Does it take a chunks out of your day? Would you like help with the research?
This baseline report was thoughtfully researched and took 10 minutes.. It's meant to be a rough draft for you to enhance with the unique insights that make you an invaluable analyst.
We just did the initial grunt work..
Are you ready to level up your skillset? Get Started Here!
Did this help you? Forward it to a friend!
you're still surfing RSS feeds? put the latest news, insights and intel, straight into your knowledge graph.
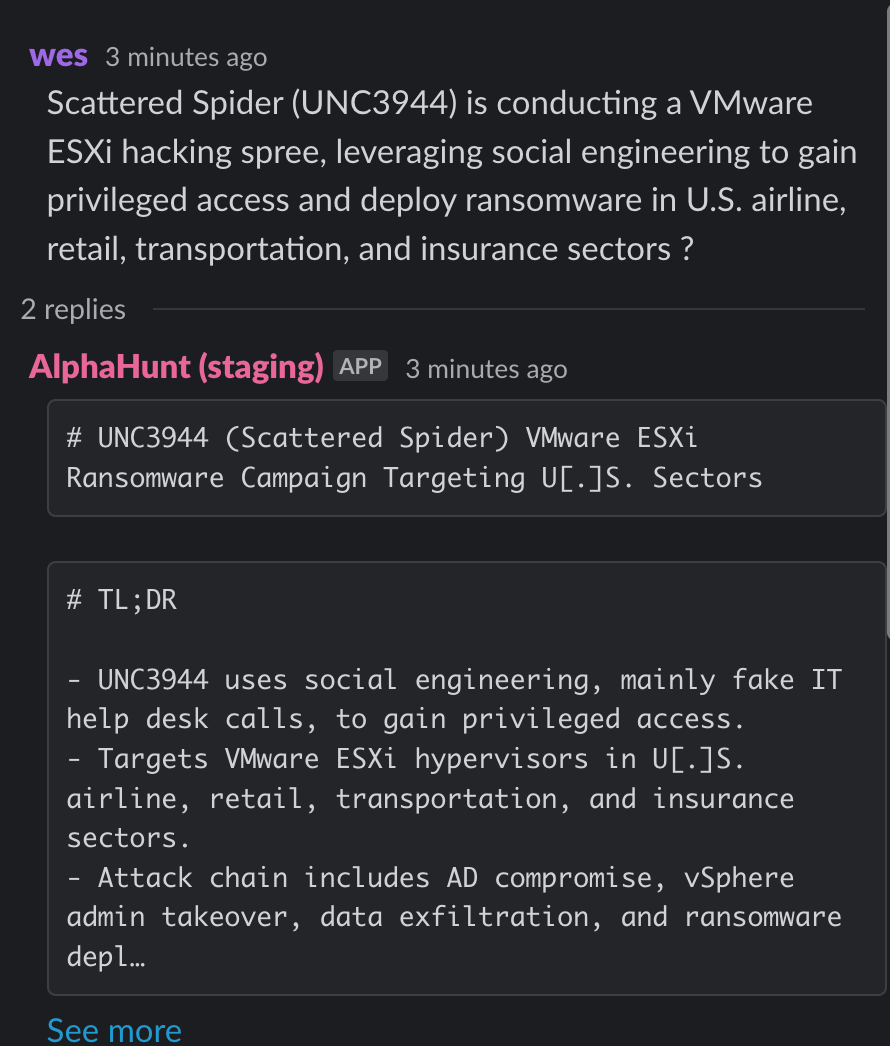
TL;DR
Key Points
-
- Ransomware groups are exploiting CVE-2024-37085 and Active Directory misconfigurations to gain hypervisor-level control over VMware ESXi, enabling mass encryption and operational disruption.
- Immediate patching, AD group management hardening, and network segmentation are critical to mitigate these attacks.
-
- Attackers leverage credential theft, lateral movement tools (Cobalt Strike, SystemBC), and social engineering (notably by UNC3944/Scattered Spider) to escalate privileges and deploy Linux-based ESXi encryptors.
- Enforcing phishing-resistant MFA, immutable backups, and real-time monitoring is essential for resilience and rapid response.
-
- Code reuse (Babuk leak), affiliate collaboration, and double-extortion tactics are accelerating ransomware evolution across critical infrastructure, manufacturing, healthcare, finance, and technology sectors.
- Organizations must adopt layered defense strategies and monitor for anomalous AD and hypervisor activity.
Executive Summary
Ransomware groups—including BlackCat/ALPHV, Black Basta, RansomHub, and Dark Angels—are increasingly targeting VMware ESXi and similar virtualization platforms using advanced hypervisor-level attack techniques. The exploitation of CVE-2024-37085, which allows attackers to create or rename an "ESX Admins" group in Active Directory and gain full administrative access to ESXi hosts, is a critical vector. Attackers combine this with credential theft (Mimikatz/Pypykatz), lateral movement (Cobalt Strike, SystemBC), and backup destruction to maximize impact and enable double-extortion.
Distinctive TTPs include the use of Linux-based ESXi encryptors (often derived from Babuk source code), SSH tunneling, and esxcli commands for payload deployment. Social engineering remains a key access vector, especially for UNC3944/Scattered Spider, which specializes in help desk impersonation and SIM swapping.
Sectoral targeting is broad, with critical infrastructure, manufacturing, healthcare, finance, and technology organizations at heightened risk. Defensive gaps—such as unpatched ESXi hosts, over-permissive AD group management, lack of MFA, and insufficient network segmentation—are routinely exploited.
Recommended mitigations include immediate patching of CVE-2024-37085, hardening AD group management, enforcing phishing-resistant MFA, segmenting management networks, deploying SIEM/XDR for real-time monitoring, and maintaining immutable, isolated backups. Organizations should also invest in security awareness training and incident response planning to counter evolving ransomware tactics.
Forecasts indicate continued escalation of hypervisor-level ransomware attacks, with new variants, increased affiliate collaboration, and the likely adoption of AI-enhanced social engineering and evasion techniques. Proactive, layered defense and continuous monitoring are essential to mitigate these evolving threats.
Deep Technical Analysis of Ransomware Groups Adopting Hypervisor-Level Attack Techniques Against VMware ESXi and Comparable Virtualization Platforms
1. Initial Access Vectors and Privilege Escalation Methods
- Ransomware groups such as BlackCat/ALPHV, Black Basta, RansomHub, and Dark Angels gain initial access primarily through phishing campaigns, malware infections (e.g., Qakbot), exploitation of vulnerabilities in exposed management interfaces, and abuse of Active Directory (AD) permissions.
- Privilege escalation is often achieved by exploiting vulnerabilities in ESXi hypervisors joined to AD domains, such as CVE-2024-37085, which allows attackers to create or rename a domain group named "ESX Admins," granting full administrative access to ESXi hosts.
- Attackers also use credential theft tools like Mimikatz or its Python variant Pypykatz, lateral movement tools such as Cobalt Strike, and persistence implants like SystemBC.
- Social engineering remains a key tactic for groups like UNC3944 (Scattered Spider), which use SMS phishing, SIM swapping, and impersonation of help desk personnel to gain access.
2. Technical Mechanisms for Targeting Hypervisors
- Exploitation of CVE-2024-37085 is a critical vector: VMware ESXi hypervisors joined to AD domains grant full administrative access to any member of a domain group named "ESX Admins" without validating the group's existence or security identifier (SID).
- Threat actors create this group and add themselves to it, gaining full control over the hypervisor.
- Attackers use esxcli commands and SSH tunneling to deploy ransomware payloads and encrypt the ESXi file system, rendering hosted virtual machines inoperable.
- Backup destruction or encryption is common to prevent recovery.
- Data exfiltration is used for double-extortion tactics.
- Lateral movement to non-virtualized systems is also observed.
3. Distinctive TTPs Compared to UNC3944 (Scattered Spider)
| Group | Initial Access & Privilege Escalation | Hypervisor Targeting Techniques | Distinctive TTPs Compared to UNC3944 |
|---|---|---|---|
| UNC3944 | Social engineering (SMS phishing, SIM swapping), help desk impersonation | Less focus on direct hypervisor exploits; uses social engineering to gain access | Heavy use of social engineering and telephone-based tactics; less direct exploitation of hypervisor vulnerabilities |
| BlackCat/ALPHV | Malware infections, exploitation of vulnerabilities, credential theft | Linux-based ESXi encryptors, exploitation of AD misconfigurations | Use of Linux encryptors for ESXi, direct exploitation of CVE-2024-37085, broader ransomware toolkit |
| Black Basta | Malware infections (Qakbot), lateral movement with Cobalt Strike | Exploitation of CVE-2024-37085, creation of ESX Admins group | Use of advanced post-exploitation tools, persistence implants, and backup destruction |
| RansomHub | Affiliate operations, social engineering, malware infections | Similar hypervisor targeting as BlackCat, use of Linux encryptors | Collaboration with other groups, shared operational playbooks |
| Dark Angels | Malware infections, exploitation of vulnerabilities | ESXi-specific ransomware variants, backup destruction | Escalated scale and ransom demands, refined hypervisor targeting |
4. Overlap in Toolsets, Code Reuse, or Operational Playbooks
- Babuk ransomware source code leak influenced the development of Linux-based ESXi encryptors used by BlackCat and others.
- Common use of tools like AnyDesk, TeamViewer for remote access, Cobalt Strike for lateral movement, and credential theft tools (Mimikatz/Pypykatz).
- Shared exploitation of AD group misconfigurations and centralized identity systems.
- Double-extortion playbooks involving data exfiltration and backup destruction are common.
- Collaboration and affiliate relationships exist, e.g., UNC3944 was a RansomHub affiliate, and DragonForce ransomware operators claimed control of RansomHub.
5. Documented Incident Timelines and Sectoral Targeting
- Timeline:
- 2021: Babuk and LockBit introduce ESXi-specific encryptors.
- Late 2021-2022: BlackCat, Black Basta, DarkSide, and REvil develop hypervisor-specific variants.
- 2023: Scattered Spider cripples over 100 hypervisors; Dark Angels and RansomHub escalate tactics.
- 2024: New families like Play, Eldorado, and SEXi continue the trend.
- 2024 (Microsoft observed): Storm-0506 used CVE-2024-37085 to deploy Black Basta ransomware in a North American engineering firm.
- Sectoral Targeting:
- Critical infrastructure, manufacturing, healthcare, finance, government, telecommunications, retail, and technology sectors.
- UNC3944 targets telecommunications, financial services, retail, and technology sectors, often focusing on large enterprises with outsourced IT.
- Retail organizations increasingly targeted for their PII and financial data.
6. Defensive Gaps Exploited and Technical Mitigations Recommended
(Subscribe to see more!)
Recommendations, Actions, Suggested Pivots, Forecasts and Next Steps
(Subscribers Only)
6. Defensive Gaps Exploited and Technical Mitigations Recommended (Cont..)
- Defensive Gaps:
- Unpatched ESXi hypervisors vulnerable to CVE-2024-37085.
- Over-permissive AD group management allowing creation of "ESX Admins."
- Lack of multi-factor authentication (MFA) on privileged accounts.
- Insufficient network segmentation and monitoring of hypervisor environments.
- Limited visibility into hypervisor behavior and insufficient backup protections.
- Mitigations:
- Apply VMware security updates addressing CVE-2024-37085 immediately.
- Harden AD group management; validate and restrict "ESX Admins" group membership.
- Enforce MFA and passwordless authentication for privileged accounts.
- Segment networks to isolate hypervisor and management interfaces.
- Monitor hypervisor logs and behaviors with SIEM/XDR solutions.
- Harden ESXi configurations (e.g., disable automatic addition of ESX Admins group).
- Maintain isolated, immutable backups and develop recovery plans.
- Educate staff on social engineering and implement positive identity verification processes.
- Use endpoint detection and response (EDR) tools to detect lateral movement and credential theft.
Recommendations, Actions, and Next Steps
-
Patch and Harden VMware ESXi Hypervisors and Active Directory Integration with Granular Controls
- Actions: Immediately apply VMware’s official security update for CVE-2024-37085 to all ESXi hypervisors. Audit Active Directory for the "ESX Admins" group; if present, validate all members and restrict group creation/renaming permissions to Tier 0 admins only. Disable the ESXi setting
Config.HostAgent.plugins.hostsvc.esxAdminsGroupAutoAddto prevent automatic privilege assignment. Reference VMware’s vSphere Security Configuration Guide for best practices, and implement application allowlisting on ESXi hosts to block unauthorized binaries. - Expected Impact: Directly mitigates the most critical privilege escalation vector exploited by BlackCat, Black Basta, and Storm-0506, preventing mass encryption and lateral movement. Reduces the risk of business-wide outages and data loss.
- Challenges: Potential downtime during patching, legacy system compatibility, and the need for cross-team coordination. Some organizations may lack visibility into all AD-integrated ESXi hosts.
- Metrics for Success: 100% of ESXi hosts patched within 7 days; no unauthorized "ESX Admins" group or anomalous group changes detected in AD; SIEM alerts for any group creation/renaming events; regular compliance checks against VMware’s security benchmarks.
- MITRE ATT&CK IDs: T1078, T1068, T1136.
- Evidence: “Microsoft recommends organizations that use domain-joined ESXi hypervisors to apply the security update released by VMware to address CVE-2024-37085.” (Microsoft Security Blog, 2024-07-29)
- Actions: Immediately apply VMware’s official security update for CVE-2024-37085 to all ESXi hypervisors. Audit Active Directory for the "ESX Admins" group; if present, validate all members and restrict group creation/renaming permissions to Tier 0 admins only. Disable the ESXi setting
-
Enforce Multi-Factor Authentication (MFA), Network Segmentation, and Privileged Access Controls for Virtual Infrastructure
- Actions: Mandate phishing-resistant MFA (e.g., FIDO2, hardware tokens) for all privileged accounts accessing ESXi, vCenter, and AD. Remove legacy authentication methods (SMS, phone, email) for admin users. Segment management networks using firewalls to restrict access to hypervisor and backup interfaces to only trusted admin workstations (PAWs). Implement strict firewall rules to block direct internet access to management interfaces and restrict remote access tools (e.g., AnyDesk, TeamViewer) to approved, monitored channels. Reference VMware’s network isolation best practices and Google/Mandiant’s guidance.
- Expected Impact: Prevents credential theft, lateral movement, and remote access tool abuse, which are common in Black Basta, UNC3944, and RansomHub campaigns. Reduces the likelihood of ransomware spreading from virtual to physical environments.
- Challenges: May require investment in MFA solutions, user training, and network re-architecture. Operational resistance due to perceived complexity or productivity impact.
- Metrics for Success: 100% privileged accounts protected by phishing-resistant MFA; no direct internet access to management interfaces; SIEM/XDR logs show no unauthorized remote access attempts; regular network segmentation validation.
- MITRE ATT&CK IDs: T1110, T1021, T1556.
- Evidence: “Enforce multifactor authentication (MFA) on all accounts, remove users excluded from MFA, and strictly require MFA from all devices, in all locations, always.” (Microsoft Security Blog, 2024-07-29); “Restrict access to ESXi hosts / vCenter Server Appliances. Ensure that backups of virtual machines are isolated, secured and immutable if possible.” (Google Cloud Blog, 2025-05-06)
-
Deploy Real-Time Monitoring, Immutable Backups, and Security Awareness Programs to Ensure Resilience and Rapid Response
- Actions: Integrate SIEM/XDR solutions to monitor ESXi and AD logs for suspicious group changes, esxcli/SSH activity, and backup tampering. Implement immutable, isolated backups for all virtual machines and critical data, with regular recovery testing and access controls that separate backup credentials from production AD. Conduct targeted security awareness training for IT, help desk, and admin staff, focusing on social engineering, identity verification, and incident reporting. Reference Cloud Security Alliance’s guidance for layered defense and backup best practices.
- Expected Impact: Enables early detection and rapid response to ransomware activity, limits the impact of double-extortion and backup destruction, and ensures business continuity even after a successful attack. Increases organizational resilience and reduces recovery time.
- Challenges: Requires investment in monitoring and backup infrastructure, ongoing staff training, and regular testing. Ensuring backup isolation from compromised credentials can be complex.
- Metrics for Success: All critical assets monitored in real time; detection of unauthorized hypervisor or AD changes within 24 hours; successful restoration from immutable backups in quarterly tests; >90% staff completion of security training with post-training assessment scores above 80%.
- MITRE ATT&CK IDs: T1562, T1486, T1087, T1204.
- Evidence: “Monitor hypervisor logs and behaviors with SIEM/XDR solutions. Maintain isolated, immutable backups and develop recovery plans. Educate staff on social engineering and implement positive identity verification processes.” (Cloud Security Alliance, 2025-06-25)
Suggested Pivots
-
In large enterprises and cloud service providers using VMware ESXi hypervisors joined to Active Directory, what specific Active Directory group management policies and monitoring controls can effectively prevent unauthorized creation or renaming of the "ESX Admins" group exploited in CVE-2024-37085 attacks? How can these controls be integrated with SIEM/XDR solutions for real-time alerting?
-
How are ransomware groups such as Storm-0506, Black Basta, UNC3944, and others evolving their initial access and lateral movement techniques post-exploitation of VMware ESXi hypervisors? What new malware variants, tools (e.g., Cobalt Strike, SystemBC), or social engineering tactics are being incorporated into their operational playbooks, particularly in sectors like critical infrastructure, manufacturing, and finance?
-
What are the most effective real-time detection and response mechanisms for identifying hypervisor-level ransomware activity, including anomalous esxcli commands, SSH tunneling, and vCenter Server event anomalies? How can organizations implement layered defense strategies combining proactive hardening, identity and access management, and advanced monitoring to mitigate these threats?
Forecast
Short-Term Forecast (3-6 months)
Ransomware groups targeting VMware ESXi hypervisors will escalate exploitation of CVE-2024-37085, leveraging Active Directory misconfigurations to create or rename the "ESX Admins" group and gain full administrative control over hypervisors. This will result in increased ransomware deployments using Linux-based ESXi encryptors, particularly impacting critical infrastructure, manufacturing, healthcare, finance, and telecommunications sectors. Attackers will continue to combine credential theft tools (Mimikatz/Pypykatz), lateral movement frameworks (Cobalt Strike), and persistence implants (SystemBC) to maximize operational impact. Social engineering campaigns, especially by UNC3944, will remain prevalent for initial access, targeting help desk personnel and privileged users. Defensive gaps such as unpatched ESXi hosts, lack of phishing-resistant MFA, and insufficient network segmentation will be aggressively exploited. Organizations that delay patching or fail to harden AD group management will face heightened risk of operational outages, data loss, and double-extortion ransomware attacks.
Examples
- The 2024 Black Basta ransomware attack on a North American engineering firm exploiting CVE-2024-37085 to deploy ransomware.
- The 2023 Scattered Spider campaign disabling over 100 hypervisors via social engineering and lateral movement.
- Babuk ransomware source code leak catalyzing proliferation of Linux-based ESXi encryptors among multiple ransomware groups.
- The June 2025 CISA advisory updating TTPs of Play ransomware group, highlighting ongoing evolution of ransomware targeting virtualized environments. (CISA Advisory, 2025-06-04)
What to watch out for
- Unauthorized creation or renaming of the "ESX Admins" group in Active Directory.
- Increased phishing and social engineering attempts targeting IT help desks and privileged users.
- SIEM/XDR alerts indicating anomalous esxcli commands, SSH tunneling, or backup tampering on ESXi hosts.
- Delays or failures in applying VMware security updates addressing CVE-2024-37085.
- Reports of ransomware incidents involving ESXi hypervisors in critical sectors.
Long-Term Forecast (12-24 months)
Ransomware threat actors will evolve hypervisor-level attack techniques, integrating more sophisticated evasion and persistence mechanisms tailored to virtualized environments. New ransomware families or variants are expected to emerge, featuring modular Linux-based encryptors capable of targeting multiple virtualization platforms beyond VMware ESXi. Exploitation of Active Directory and centralized identity systems will remain a core vector, but attackers will increasingly adopt AI-enhanced tools to automate detection evasion, lateral movement, and social engineering. While direct evidence of AI-driven lateral movement in ransomware is currently limited, recent trends in AI-powered social engineering—including deepfake audio and video impersonations—are already documented and likely to be weaponized further by threat actors. Defensive strategies will mature, with widespread adoption of phishing-resistant MFA, network micro-segmentation, and real-time hypervisor behavior analytics becoming standard. Organizations that do not invest in immutable backup solutions and continuous monitoring will remain vulnerable to high-impact double-extortion ransomware campaigns. Collaboration among ransomware affiliates will intensify, sharing operational playbooks and tooling, complicating attribution and defense.
Examples
- Evolution from Babuk to BlackCat/ALPHV ransomware families demonstrating code reuse and operational collaboration.
- Increasing use of AI-powered social engineering and deepfake impersonation in cybercrime, as reported by CrowdStrike and Akamai in 2025. (CrowdStrike, 2025-01-16)
- Adoption of immutable backup and zero-trust network segmentation frameworks in leading enterprises to mitigate ransomware risks.
- FBI and CISA warnings on Scattered Spider’s evolving tactics, including multifactor phishing and social engineering enhancements. (Cybersecurity Dive, 2025-07-29)
What to watch out for
- Emergence of new ransomware variants targeting multiple hypervisor platforms with enhanced encryption and evasion capabilities.
- Increased sophistication in social engineering attacks, including AI-generated voice or video deepfakes.
- Adoption rates of phishing-resistant MFA and network segmentation controls in enterprise environments.
- Development and deployment of advanced SIEM/XDR solutions with hypervisor-specific detection capabilities.
- Public disclosures or leaks of ransomware affiliate operational playbooks indicating collaboration trends.
MITRE ATT&CK IDs
T1136.002, T1486, T1562, T1021.004, T1204, T1556, T1078, T1068, S0002, S0154, S0663, M1026, M1030, M1053
Appendix
References
- (2024-07-29) - Ransomware operators exploit ESXi hypervisor vulnerability for mass encryption - Microsoft Security Blog
- (2025-05-06) - Defending Against UNC3944: Cybercrime Hardening Guidance from the Frontlines - Google Cloud Blog
- (2025-06-25) - ESXi Ransomware: The Growing Threat to Virtualized Environments - Cloud Security Alliance
- (2024-07-29) - VMware Security Advisory for CVE-2024-37085
- (2024) - VMware vSphere Security Configuration Guide
- (2025-06-04) - #StopRansomware: Play Ransomware | CISA
- (2025-01-16) - Most Common AI-Powered Cyberattacks | CrowdStrike
- (2025-07-29) - FBI, CISA warn about Scattered Spider's evolving tactics - Cybersecurity Dive
AlphaHunt
(Have feedback? Did something resonate with you? Did something annoy you? Just hit reply! :))
Have a ESXi Environment- not sure what these headlines mean??
- Scattered Spider (UNC3944) is conducting a VMware ESXi hacking spree, leveraging social engineering to gain privileged access and deploy ransomware in U.S. airline, retail, transportation, and insurance sectors ?
Does it take a chunks out of your day? Would you like help with the research?
This baseline report was thoughtfully researched and took 10 minutes.. It's meant to be a rough draft for you to enhance with the unique insights that make you an invaluable analyst.
We just did the initial grunt work..
Are you ready to level up your skillset? Get Started Here!
Did this help you? Forward it to a friend!
(c) 2025 CSIRT Gadgets, LLC
MITRE ATT&CK
Techniques
-
[T1136.002] Create Account: Domain Account – Attackers exploit Active Directory to create or rename a domain group named "ESX Admins," granting themselves administrative access to ESXi hypervisors, central to CVE-2024-37085 exploitation.
- Create Account: Domain Account
- Supported by: Microsoft Security Blog
-
[T1486] Data Encrypted for Impact – Ransomware groups deploy Linux-based encryptors to ESXi, encrypting virtual machine data and demanding ransom for decryption.
- Data Encrypted for Impact
- Supported by: Cloud Security Alliance
-
[T1562] Impair Defenses – Attackers destroy or encrypt backups and disable security tools to prevent recovery and detection, a common tactic in these campaigns.
- Impair Defenses
- Supported by: Cloud Security Alliance
-
[T1021.004] Remote Services: SSH – SSH is used for lateral movement to ESXi hypervisors, enabling attackers to deploy ransomware payloads and execute commands.
- Remote Services: SSH
- Supported by: Sygnia
-
[T1204] User Execution – Initial access is often gained via phishing and social engineering, including malicious links and attachments.
- User Execution
- Supported by: Google Cloud Blog
-
[T1556] Modify Authentication Process – Abuse of authentication mechanisms, such as manipulating AD group membership or bypassing MFA, to escalate privileges and maintain access.
- Modify Authentication Process
- Supported by: Microsoft Security Blog
Tactics
-
[TA0001] Initial Access – Phishing, exploitation of exposed management interfaces, and social engineering are primary entry points.
- Initial Access
- Supported by: Google Cloud Blog
-
[TA0004] Privilege Escalation – Exploiting AD misconfigurations and CVE-2024-37085 to gain elevated access on ESXi.
- Privilege Escalation
- Supported by: Microsoft Security Blog
-
[TA0040] Impact – Encrypting data, destroying backups, and causing operational outages are the core objectives.
- Impact
- Supported by: Cloud Security Alliance
Procedures
-
[T1136.002] Create Account: Domain Account – Creation or renaming of the "ESX Admins" group in AD to exploit CVE-2024-37085 and gain hypervisor control.
-
[T1486] Data Encrypted for Impact – Use of ESXi-specific ransomware encryptors to lock virtual machines and demand ransom.
-
[T1562] Impair Defenses – Destruction or encryption of backups and disabling of security controls to maximize impact.
Software
-
[S0002] Mimikatz – Used for credential theft to facilitate privilege escalation and lateral movement in AD-integrated environments.
-
[S0154] Cobalt Strike – Used for post-exploitation, lateral movement, and deploying ransomware payloads to ESXi and other systems.
-
[S0663] SystemBC – Used for persistence and command-and-control in ransomware operations targeting virtualized infrastructure.
Mitigations
-
[M1026] Privileged Account Management – Restrict creation and modification of privileged groups like "ESX Admins" in AD and monitor for unauthorized changes.
-
[M1030] Network Segmentation – Isolate management interfaces for ESXi and backup systems to prevent lateral movement and remote exploitation.
-
[M1053] Data Backup – Maintain isolated, immutable backups to ensure recovery from ransomware attacks targeting hypervisors and virtual machines.
Groups
- [G1015] UNC3944 (Scattered Spider)
- UNC3944, also known as Scattered Spider, is a financially motivated threat actor specializing in social engineering, initial access via phishing, and targeting virtualized environments.
- UNC3944 (Scattered Spider)