deep
[DEEP RESEARCH] The Token Was Not a Session. It Was a Signing Dependency.
New NIST guidance exposes a containment gap: the revocation command can succeed while an attacker’s access survives.
deep
New NIST guidance exposes a containment gap: the revocation command can succeed while an attacker’s access survives.
weekly
The engineer called it internal; the attacker found it internet-adjacent. Inventory and patch exposed GS1900 and Conductor gear, then hunt job changes and secret access.
forecasts
Two incidents appear to clear the bar. Govern AI credentials by replay value and blast radius before access becomes impact.
deep research
A practical operating model for package admission, runtime detection, and proving downstream impact before the trail goes cold.
weekly
Patch the control plane, then hunt leaked authority: new admins, fresh tokens, API use from new origins. Copied keys can outlive a green patch dashboard.
gametheory
The attacker needs sustained, useful output. Defenders can turn that dependency into friction across the access ecosystem.
gametheory
Shared intrusion logistics can be a better chokepoint than one APT—if defenders can prove real control-plane dependence.
weekly
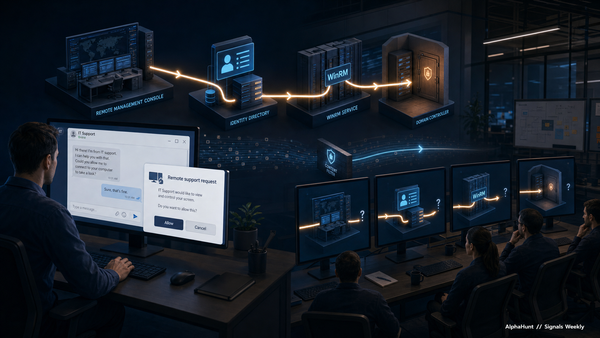
A Teams message from “IT” can now be the first step in a domain takeover: remote-support session, silent install, then AD and WinRM movement.

forecasts
Our 45% forecast—and the public signals that would show private cyber effects have moved from authority to action.
gametheory
Vishing works because urgency can become SaaS authority. Break the trust transaction without breaking support.
weekly
Three clocks are running: active PaperCut exploitation, QTFY infrastructure rebuilding after disruption, and AI-agent activity outpacing log governance. Hunt the transitions—not the tidy incident story.
forecasts
We put a 35% chance on two more extortion crews adopting decentralized victim infrastructure by June 2027.